CoCo Expands Across Emerging Bubble Tea Markets with Hungary and Armenia Openings and Planned Ukraine Debut
Image File
Original HTML

CoCo Expands Across Emerging Bubble Tea Markets with Hungary and Armenia Openings and Planned Ukraine Debut

TAIPEI, Oct. 27, 2026 /PRNewswire/ -- Leading global boba tea brand CoCo Bubble Tea, with more than 5,000 stores worldwide, has opened its first stores in Hungary and Armenia and is preparing to debut in Ukraine with a Kyiv location planned to open in late December. As CoCo approaches its 30th anniversary in 2027, the three-market rollout advances CoCo's franchise expansion across emerging bubble tea markets in Central and Eastern Europe and the South Caucasus, combining local consumer insight with market-specific menu planning and regional operational support.

CoCo sees growing interest in international food and beverage concepts and Asian-inspired drinks across these markets, particularly among younger consumers. The company believes customization, social media discovery and the continued development of café culture can support the category's long-term growth. Persistence Market Research estimates that the European bubble tea market will grow from $727.2 million in 2026 to $1.26 billion by 2033, with demand supported by innovative and customizable beverages.

Local Insight Shapes Market Expansion

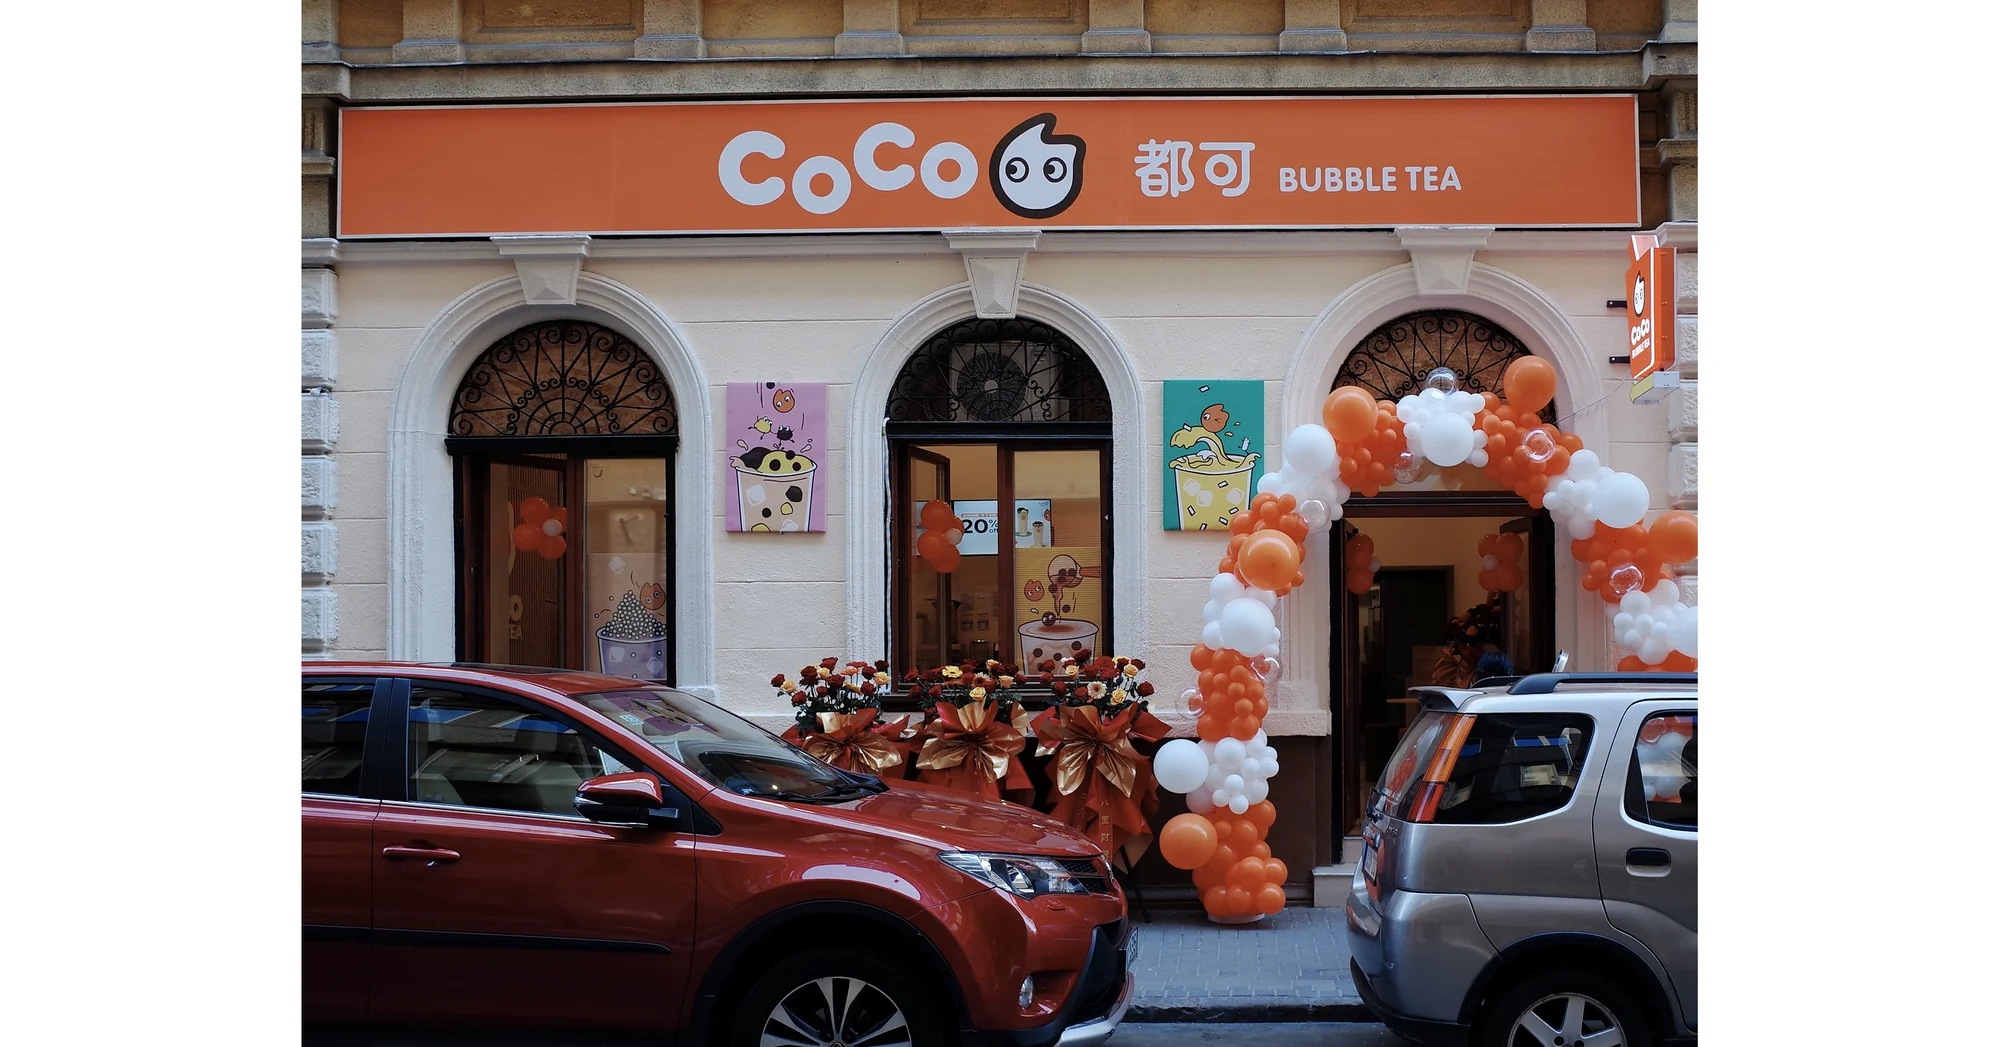
CoCo's first store in Hungary opened May 20 at Dohány u. 28, 1074 Budapest. The location offers CoCo's European menu. The launch included Hungarian-language content on Facebook and Instagram and limited merchandise for early customers. The store is also available for delivery through Wolt. These activities combine CoCo's global brand platform with locally relevant ways to introduce the menu and reach consumers.

The Yerevan store opened July 15 at 2 Hin Yerevantsi St., on the second floor. The local team is using Facebook and Instagram to introduce products, feature customer experiences and encourage reviews and feedback. CoCo is also providing on-site operational support for the Yerevan store.

Across new markets, CoCo works with local franchise partners to study the competitive landscape and consumer preferences. The brand retains its classic drinks while adjusting the product mix where appropriate. Depending on local demand, this may include a greater selection of fruit teas, refreshing flavors or coffee drinks. Feedback after opening can inform further menu and marketing adjustments.

CoCo is also preparing its first store in Ukraine in Kyiv. Its market plan includes mall and kiosk formats with self-ordering capabilities. Hungary and Ukraine are priority markets for CoCo's continued development in Central and Eastern Europe, while Armenia provides a base for exploring further opportunities in the South Caucasus and neighboring West Asian markets.

Operations in Hungary and preparations for the Ukraine opening are supported by CoCo's European warehouse and supply chain network. The network supports ingredient supply and store operations across the region. In Armenia, support is delivered locally. These regional capabilities are combined with CoCo's established training, product development and store management systems.

CoCo plans to develop at least three stores in each of the three markets over time. To accelerate regional growth, the brand is actively seeking qualified master franchise partners and particularly welcomes established multi-unit retail and F&B operators with proven market experience. CoCo is also actively exploring further market development across Central and Eastern Europe, the Middle East and South Africa.

Entrepreneurs and operators interested in franchise opportunities can learn more at https://www.coco-tea.com/Franchise.

About CoCo Bubble Tea

Founded in 1997, CoCo Bubble Tea is a global bubble tea industry leader with a network of more than 5,000 stores across major markets worldwide, including North America, Europe, Asia, and Oceania. Approaching its 30th anniversary milestone, CoCo is recognized for its commitment to premium tea craftsmanship, consistent preparation standards, and relentless beverage innovation. The brand continues to scale its international footprint through robust supply chain capabilities, corporate-owned flagship operations, and strategic master franchise partnerships. For more information, visit https://www.coco-tea.com/.

Share this article

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302920222
Press Eligible
Yes
Press Eligible Reason
Manuelle Prüfung nötig. Risiko: MEDIUM. Flags: ['numbers']. Stichprobe: False
Source Name
Unknown Company
Original Summary

<p>TAIPEI, Oct. 27, 2026 /PRNewswire/ -- Leading global boba tea brand CoCo Bubble Tea, with more than 5,000 stores worldwide, has opened its first stores in Hungary and Armenia and is preparing to debut in Ukraine with a Kyiv location planned to open in late December. As CoCo approaches its...</p>

Image URL
https://mmx.prnewswire.com/media/MS2018687/20261022002417EDT_image_2.jpg?id=OA3041264&p=facebook
Content Hash (SHA-256, erste 32 hex)
bd4f1413450f8ca7a458fa920e7717be
3TREES Shines at Big 5 Construct Kenya, Showcasing Healthy Living Solutions for East Africa
Image File
Original HTML

3TREES Shines at Big 5 Construct Kenya, Showcasing Healthy Living Solutions for East Africa

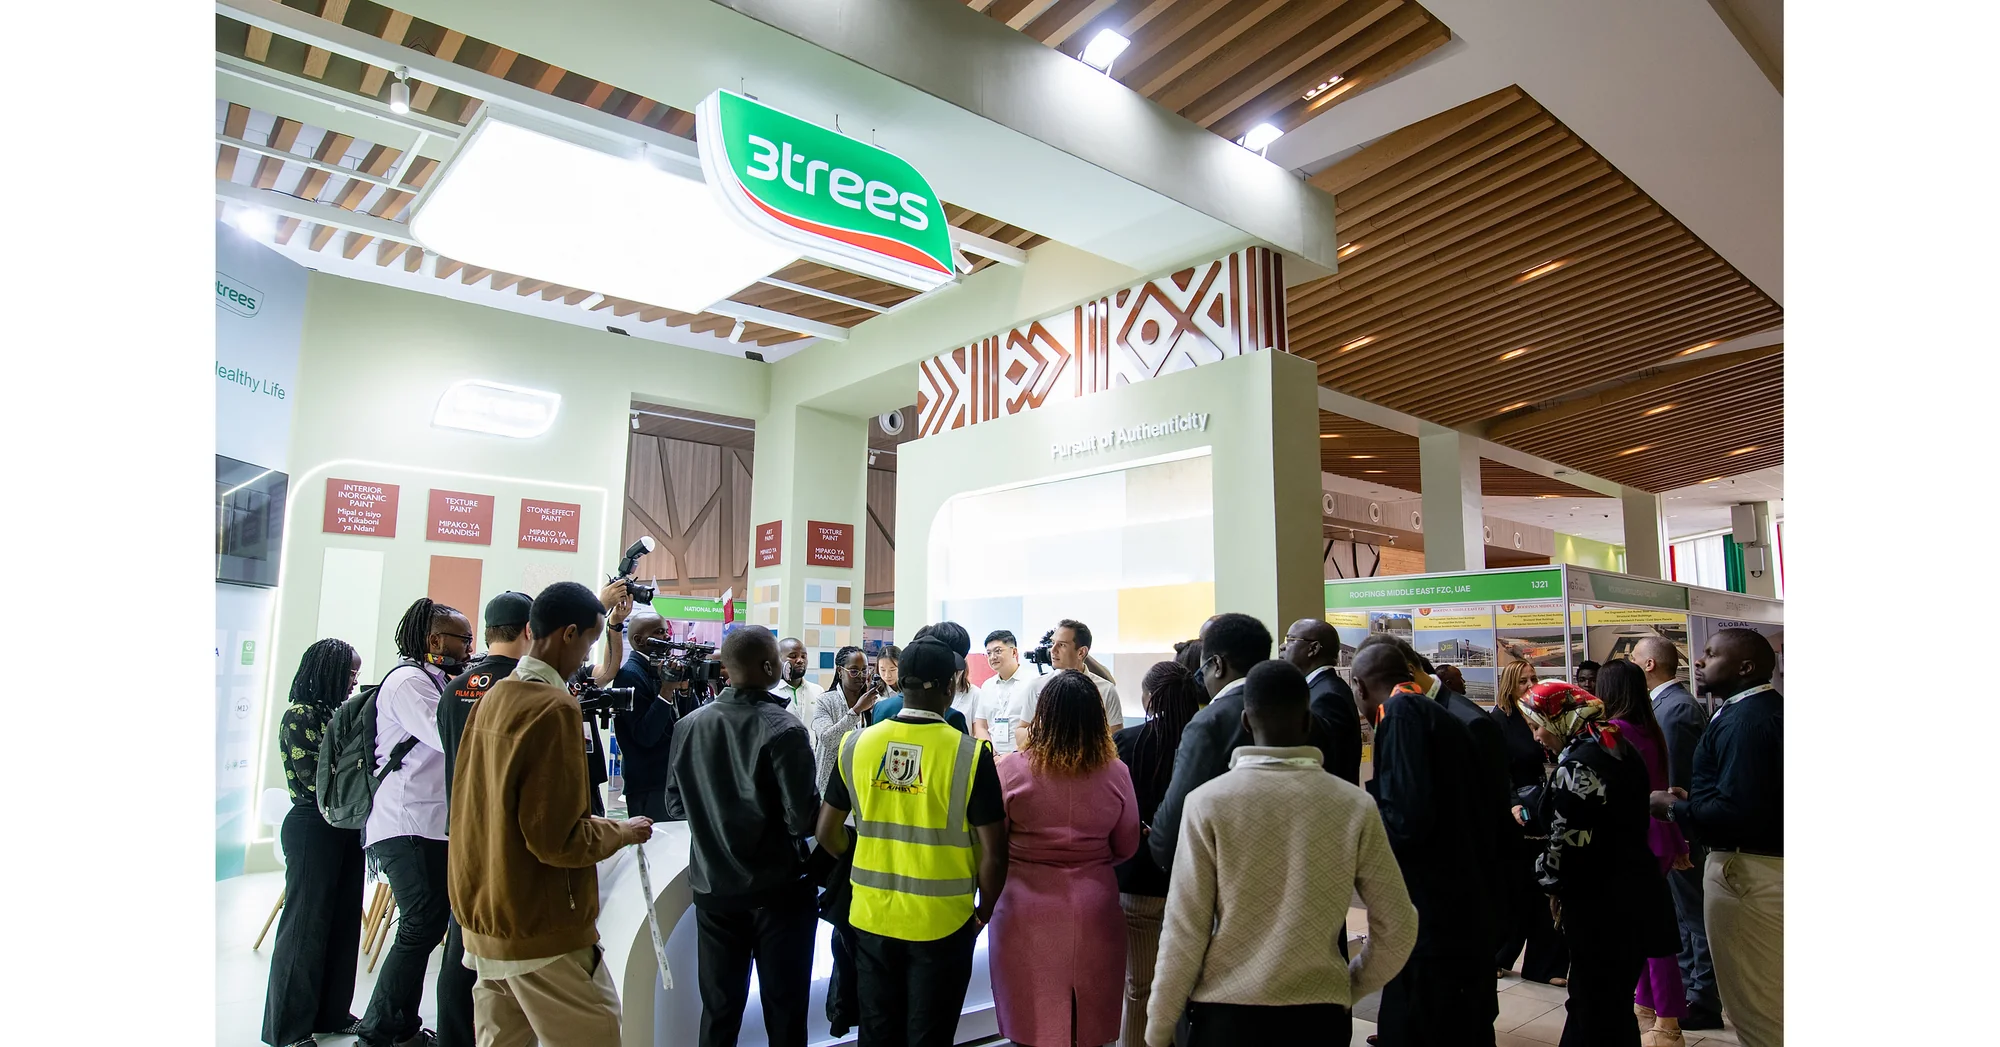
PUTIAN, China, Oct. 27, 2026 /PRNewswire/ -- 3TREES recently showcased its green coating solutions at Big 5 Construct Kenya, a major building and construction trade show in East Africa that opened on October 21, 2026, at the Sarit Expo Centre in Nairobi. Guided by its "Create Healthy Life" philosophy, 3TREES presented a broad product portfolio at Hall 1, Booth 1J17, attracting strong interest and active business discussions. The event also strengthened the brand's visibility among regional customers and industry partners.

The exhibition marked another step in 3TREES' expansion in East Africa. Continued infrastructure investment and urbanization across the region are driving demand for building materials that are environmentally friendly, healthy, durable and suited to local conditions. Through the exhibition, 3TREES introduced integrated green coating solutions for regional construction needs.

The product showcase covered stone-effect exterior coatings, inorganic interior coatings, artistic finishes, waterproofing membranes and coatings, and floor coatings. Together, these products demonstrated 3TREES' capabilities across wall and floor applications and helped visitors gain a clearer understanding of the company's product quality, technologies and service strengths.

The booth welcomed distributors, engineering purchasers, contractors and industry professionals from Kenya, Tanzania, Uganda, Ethiopia and other East African markets. Visitors discussed product performance, application methods, technical standards, local adaptability and distribution cooperation with the 3TREES team. Through one-to-one consultations, the team introduced key technologies and application scenarios while sharing experience from engineering and residential projects in China. The exchanges generated positive feedback and opportunities for further cooperation.

Looking ahead, 3TREES will continue adapting its product formulations and coating solutions to East Africa's high temperatures, intense ultraviolet exposure, concentrated rainy seasons and local construction standards. The company will also advance regional channel development and strengthen technical support and after-sales services to better serve local customers.

Building on its research and development strengths and broad product portfolio, 3TREES will deepen industry exchange and strategic cooperation, introduce mature green coating technologies and solutions to more overseas markets, and support the green development of East Africa's building materials industry. Through sustained localization, the company aims to bring healthier and greener products to more households and construction projects across the region.

Follow us:

WEB: https://www.3treesgroup.com/en/

Facebook: 3Trees PaintâGlobal

Twitter:â3Trees

Instagram:â3treespaintofficial

TikTok: 3TreesPaints Global

Contact us:

TEL: 400-8823-777

Email: [email protected]

Share this article

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
prn_302920228
Press Eligible
Yes
Press Eligible Reason
Company news about 3TREES showcasing building-material products and developing business in East Africa.
Source Name
Unknown Company
Original Summary

<p>PUTIAN, China, Oct. 27, 2026 /PRNewswire/ -- 3TREES recently showcased its green coating solutions at Big 5 Construct Kenya, a major building and construction trade show in East Africa that opened on October 21, 2026, at the Sarit Expo Centre in Nairobi. Guided by its "Create Healthy...</p>

Image URL
https://mmx.prnewswire.com/media/MS2021425/20261026214319EDT_image_1.jpg?id=OA3041306&p=facebook
Content Hash (SHA-256, erste 32 hex)
c64f7bdcd1d7c396aa3580d27d1d1acf
deviceWISE® Intelligence Suite Turns Video into Operational Action with NVIDIA VSS Blueprint
Image File
Original HTML

Platforms

deviceWISE® Intelligence Suite Turns Video into Operational Action with NVIDIA VSS Blueprint

By Imad Hourani

June 1, 2026

Estimated reading time: 5 minutes

Manufacturers who embed visual monitoring directly into their operational systems accelerate detection-to-action time and ensure product consistency across lines. Incorporating visual intelligence with factory data and workflows prevents data isolation and streamlines decision-making.

The deviceWISE Intelligence Suite enables real-time operational gains by deploying industrial AI agents at the operational edge. Working across machine data and enterprise applications, these agents interpret production data and proactively support business-critical decisions.

Integrating NVIDIA Metropolis Video Search and Summarization (VSS) Blueprint adds scalable visual intelligence to this system.

When a camera flags a deviation on a production line, the immediate questions are operational. Does the event relate to a known machine condition? What should happen next? Answering these questions requires live machine data, process history and the operational logic that guides the factory’s response.

The deviceWISE Intelligence Suite transforms manufacturers’ approach from passive observation to active, real-time intelligence. The platform connects PLCs, robots, CNCs and enterprise systems, delivering a real-time operational picture.

NVIDIA VSS Blueprint combines accelerated computer vision with vision-language models, including NVIDIA Cosmos, and large language models to analyze live and recorded video. Using VSS skills with coding agents, developers can build AI agents faster from natural language prompts.

With VSS Blueprint, the deviceWISE Intelligence Suite turns video into an actionable data stream, interpreted alongside machine behavior and operational history.

Using the Model Context Protocol (MCP) and NVIDIA NIM microservices, the deviceWISE Intelligence Suite connects VSS Blueprint visual insights to live machine data and process state.

The platform evaluates the situation against operational logic, then routes the response to the correct destination. NIM accelerates agent deployment by matching each task to the most effective model. Together, they embed visual intelligence into the operational flow.

When monitoring needs change on a production line, the typical path involves scoping a new analytics pipeline, building it and testing it before it reaches the floor.

NVIDIA VSS Blueprint shortens that cycle with VSS skills, a catalog of prebuilt, reusable building blocks that cover core video analytics functions. These include:

Rather than assembling a custom pipeline for each use case, developers describe their needs in natural language. A coding agent, such as Codex or Claude, assembles the appropriate skills into a working video analytics agent. NVIDIA NemoClaw blueprint provides a reference for deployment with guardrails so these agents run more safely in production environments.

Within deviceWISE, these visual capabilities come online quickly. Quality inspection and safety monitoring can be extended to new lines or layouts without rebuilding analytics. These skills fit into deviceWISE’s operational layer, linking new capabilities to existing data and response logic.

Reducing response times for safety or equipment faults requires clarity and quick action. Visual confirmation is the first step. The speed and quality of the response depend on how well the visual signal connects to the line management systems.

In a production environment, AI-powered cameras detect unsafe conditions in real time. Using advanced object detection and tracking modules, they identify:

deviceWISE adds the critical operational intelligence layer that gives meaning to these events. By combining machine data, robot status and process context, the system understands what is actually occurring rather than simply registering what is visible.

When a risk is identified, deviceWISE instantly closes the loop. The platform contextualizes the detected event, determines the severity based on real-time operations and executes appropriate action at the edge. This may involve sending a targeted alert, stopping a machine or orchestrating safety workflows. At the same time, the system captures structured data to support reporting and ongoing improvement.

This approach moves safety from reactive monitoring to real-time, automated intervention. Every event is understood, acted upon and improved.

Visual monitoring gains value when connected to operational systems. NVIDIA VSS Blueprint and the deviceWISE Intelligence Suite link visual detection to machine context and response logic in a single workflow.

Video insights are matched to live production data, evaluated against operational rules and routed to the correct location. For manufacturers focused on tightening response times and protecting consistency across lines, this integration offers a practical, scalable path forward.

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
fbfb86479be292ec554d0492c1a19071
Press Eligible
Yes
Press Eligible Reason
Manuelle Prüfung nötig. Risiko: MEDIUM. Flags: ['none']. Stichprobe: False
Source Name
Telit Cinterion
Original Summary

<p>Manufacturers who embed visual monitoring directly into their operational systems accelerate detection-to-action time and ensure product consistency across lines. Incorporating visual intelligence with factory data and workflows prevents data isolation and streamlines decision-making.  The&#160;deviceWISE&#160;Intelligence Suite enables real-time operational gains by deploying&#160;industrial AI agents&#160;at the operational edge. Working across machine data and enterprise applications, these agents...</p>
<p>The post <a href="https://www.telit.com/blog/devicewise-nvidia-vss-factory-video-intellig…® Intelligence Suite Turns Video into Operational Action with NVIDIA VSS Blueprint</a> appeared first on <a href="https://www.telit.com">Telit Cinterion</a>.</p>

Image URL
https://www.telit.com/wp-content/uploads/2025/12/dw_intel_1.jpg
Source Node
Content Hash (SHA-256, erste 32 hex)
aecd8f9f9f3a4076977f5b833da1f737
Smart Utilities: How Integrated IoT Systems Enable Smarter Utility Management
Image File
Original HTML

Modules

Smart Utilities: How Integrated IoT Systems Enable Smarter Utility Management

June 9, 2026

Estimated reading time: 5 minutes

Integrated Internet of Things (IoT) systems help to connect smart city infrastructure with smart grids. They also link smart utilities to shared data, enabling more precise monitoring through wireless IoT data collection and real-time analytics.

For example, sensors attached to a home’s water pipes can track water pressure and detect leaks. Temperature monitoring adds context for seasonal shifts or freeze risks. This helps utilities detect issues early while providing consumers with better insight into usage and potential savings.

As utilities modernize to meet rising energy demands, renewable energy and alternative distribution models become central to long-term planning. At the same time, IoT has transformed how utilities:

By using modules with networks of cost-effective sensors, utilities can:

Low-power wide-area network (LPWAN) technologies, including narrowband IoT (NB-IoT), enable long-range communication. They consume minimal power, making them well-suited for large-scale utility deployments.

As LPWAN adoption expands across the smart utilities sector, utilities benefit from:

Some organizations are also deploying high-bandwidth 5G connectivity to support applications such as:

Smart water and waste management systems help utilities reduce losses, improve service reliability and lower operational costs. Sensors deployed across water pipes, drains and treatment infrastructure provide real-time data. Utilities use this information to monitor:

Insights such as these help utilities detect anomalies earlier and prevent losses. They can also respond quickly during emergencies, such as flooding.

Cities are also adopting smart waste management solutions that use sensor data to optimize collection routes and schedules. Waste bins can alert operators when they are full, enabling more efficient truck routing to save time and fuel.

Lighting plays a significant role in energy consumption for both residential and municipal environments. IoT-enabled smart lighting systems adjust lighting levels based on real-time needs, reducing costs and improving efficiency.

In homes, smart lighting enhances security through remote and automated control while providing insights into energy usage and identifying faulty or inefficient fixtures. In cities, LPWAN-enabled lighting systems simplify maintenance across large areas such as streets and parking structures.

Sensors can adjust lighting based on environmental conditions, like fog or rain. They can also alert maintenance teams to failures and follow dynamic schedules that balance safety and energy savings.

Smart grids are digitally managed electricity networks that use IoT sensors and modern technologies to balance supply and demand more effectively. Software and analytics support that balance and help utilities act faster. Utilities use smart grids for predictive maintenance and real-time monitoring. Automated responses can also address changing conditions.

Artificial intelligence (AI)-powered analytics can process vast amounts of sensor data to optimize load distribution. The same analytics can detect outages and support emergency responses, such as to wildfires or severe weather. Over time, these systems help utilities forecast demand and monitor renewable energy integration. They also help identify potential cybersecurity threats, making smart grids a cornerstone of modern smart city initiatives.

In emergency situations, first responders can access smart grids to direct traffic or cut off and restore power as needed.

McKinsey’s 2024 Global Energy Perspective report projects global energy demand will grow by 11% to 18% by 2050. As utilities work to meet demand, integrated IoT solutions are essential to maximize energy efficiency and resilience. A smarter utility future is already unfolding. Organizations are turning to IoT deployments not only to reduce costs but also to improve service quality and strengthen infrastructure for the future.

With over 30 years of experience in IoT innovation, Telit Cinterion helps connect devices, systems and data across the global utilities ecosystem. We have a proven track record of supporting IoT solutions worldwide.

Contact us to learn how integrated IoT systems can support your smart utilities initiative. Our experts will help you find the IoT product or solution that meets your needs.

Editor’s note: This blog was originally published on 5 March 2020 and has since been updated.

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
f92e5bf73b180305a5afd696a78e62b8
Press Eligible
Yes
Press Eligible Reason
Manuelle Prüfung nötig. Risiko: MEDIUM. Flags: ['numbers']. Stichprobe: False
Source Name
Telit Cinterion
Original Summary

<p>Integrated Internet of Things (IoT) systems help to connect smart city infrastructure with smart grids. They also link smart utilities to shared data, enabling more precise monitoring through wireless IoT data collection and real-time analytics.&#160; For example, sensors attached to a home’s water pipes can track water pressure and detect leaks. Temperature monitoring adds context...</p>
<p>The post <a href="https://www.telit.com/blog/how-integrated-iot-systems-enable-smarter-ut… Utilities: How Integrated IoT Systems Enable Smarter Utility Management</a> appeared first on <a href="https://www.telit.com">Telit Cinterion</a>.</p>

Image URL
https://www.telit.com/wp-content/uploads/2021/11/Telit_Enabling-Smarter-Utilities-with-an-Integrated-Approach.jpg
Source Node
Content Hash (SHA-256, erste 32 hex)
9680f36db6528adeb4581a78ca105d5f
Cyber Resilience Act: What IoT Manufacturers Need to Know
Image File
Original HTML

Modules

Cyber Resilience Act: What IoT Manufacturers Need to Know

By Enrico Milanese

Alberto Carelli

Federico Della Valle

June 11, 2026

Estimated reading time: 10 minutes

The European Union (EU) Cyber Resilience Act (CRA) establishes mandatory cybersecurity requirements for products with digital elements placed on the European market. The regulation applies general requirements across all products, with more specific obligations for selected product categories.

For companies building connected products, this is a fundamental shift. Manufacturers must build cybersecurity into their products from the design phase and maintain it throughout the support period.

Compliance is a lifecycle security responsibility, requiring manufacturers to continuously identify, assess, and remediate vulnerabilities throughout the product support period.

With the first CRA deadline taking effect in September 2026, manufacturers of IoT products need to understand what the regulation requires and how to begin preparing.

The Cyber Resilience Act (EU) 2024/2847 is an EU Regulation that establishes mandatory cybersecurity requirements for products with digital elements, covering both hardware and software.

The CRA is the first regulation to embed cybersecurity directly into the EU product compliance and safety framework. It applies as a horizontal layer across industries and technologies.

Unlike traditional compliance schemes, the CRA introduces broader and ongoing obligations. Manufacturers must build cybersecurity into the design and development process, manage vulnerabilities, and provide security support throughout the product lifecycle.

These obligations apply at the product and system level across the supply chain. They do not transfer full responsibility to individual components or their suppliers. CRA compliance is a regulatory precondition for CE marking. Manufacturers must demonstrate that their products meet CRA cybersecurity requirements before placing them on the EU market.

The CRA takes a supply chain approach to cybersecurity, distributing responsibilities across all actors involved in bringing a product to market. Under the CRA, IoT manufacturers are expected to:

These obligations extend across the supply chain. Manufacturers, importers, distributors, and authorized representatives each carry defined compliance responsibilities.

While the CRA entered into force on 10 December 2024, requirements are being phased in over three years to complement existing regulations. Two dates are especially important for compliance planning:

11 September 2026: Obligations related to CRA vulnerability reporting take effect. Manufacturers must report actively exploited vulnerabilities and severe security incidents to EU authorities (ENISA and national CSIRTs). An early warning must be submitted within 24 hours of becoming aware of a vulnerability, followed by a detailed notification within 72 hours.

For details about the September 2026 reporting obligations, see our CRA Vulnerability Reporting: What IoT Manufacturers Need to Know Before September 2026 blog.

11 December 2027: Full CRA compliance becomes mandatory. All products with digital elements placed on the EU market after this date must demonstrate complete conformity.

Companies that begin preparing now will be better positioned to meet both milestones without disrupting their product roadmaps.

The CRA defines products with digital elements as any software or hardware product, along with its remote data processing solution, that can directly or indirectly connect to a network or another device. The regulation classifies these products into tiers that determine the conformity assessment procedure required before EU market placement.

A product’s classification directly affects whether it can be self-assessed or requires third-party evaluation. Classification depends on the product’s functionality and intended use at the final product level.

The CRA defines what IoT device manufacturers must achieve but deliberately avoids prescribing how to implement these requirements. That role belongs to European harmonized standards, which translate the regulation’s legal obligations into assessable technical and process requirements.

In April 2025, CEN, CENELEC and ETSI accepted Standardization Request M/606 from the European Commission, initiating development of 41 harmonized standards to support CRA implementation.

These standards will be delivered in two waves: 15 horizontal standards applicable across all product categories and 26 vertical standards with additional requirements tailored to specific product types.

CEN/CLC/JTC 13/WG 9 is primarily developing the horizontal standards, which follow the EN 40000‑1‑x numbering scheme. They are structured as follows:

The table below summarizes the most relevant draft horizontal standards under development as of June 2026.

Particular attention should be given to prEN 40000-1-3 on vulnerability handling. The related CRA obligations take effect on 11 September 2026, ahead of the rest of the regulation. Until harmonized standards are formally adopted as European Norms (EN) and cited in the EU Official Journal, conformity must be assessed directly against CRA Annex I. Though not yet finalized, the draft standards provide the most concrete guidance available for meeting Annex I requirements.

Vertical standards are also under active development and available for public review through resources such as the ETSI GitLab repository.

The European Commission provides official information and guidance for the CRA through:

The Commission also published a draft of its guidance document on the CRA, with public comment closing in April 2026. It covers topics including:

Assess CRA applicability across your product portfolio and role (manufacturer, importer or distributor) under the regulation.

Proactively monitor standardization developments. The EN 40000 draft series provides the emerging framework for CRA compliance. Tracking these standards as they evolve helps clarify technical and procedural requirements ahead of finalization.

Review secure development practices. Evaluate your current approach to IoT security by design and vulnerability handling, with particular attention to CRA vulnerability reporting requirements ahead of the September 2026 deadline.

Conduct product risk assessments. If formal threat analysis is not yet part of your process, establish one.

Evaluate your product lifecycle strategy. Confirm that your update strategy and product support period align with EU CRA requirements.

Key deliverables manufacturers should prepare include:

– Software Bill of Materials (SBOM) covering all software components and dependencies

– Documented vulnerability handling and disclosure process

– Defined product support period and security update policy

– Secure mechanism to ensure authenticity and integrity of firmware/software updates

– Technical documentation demonstrating compliance with CRA Annex I requirements

The CRA does not replace existing sector-specific EU legislation, nor does it merge with the Radio Equipment Directive (RED). Instead, it works alongside it.

The RED Delegated Regulation on cybersecurity (EU) 2022/30 introduced cybersecurity requirements for certain radio equipment. The EN 18031 series provides technical standards supporting compliance with those requirements.

However, to provide regulatory coherence, the cybersecurity provisions introduced under the RED Delegated Regulation are expected to be phased out to avoid overlap, with the CRA becoming the primary cybersecurity framework from 11 December 2027. From that date, all cybersecurity obligations for products with digital elements will fall under the CRA framework.

During the transitional period from 1 August 2025 to 10 December 2027, manufacturers of in-scope radio equipment must continue to comply with RED cybersecurity requirements. Beginning on 11 December 2027, the CRA will become the sole cybersecurity framework for these products.

While the CRA will address cybersecurity obligations, RED will continue to govern radio performance, electrical safety, and electromagnetic compatibility (EMC) for wireless products in the EU market.

Many of the technical controls and security principles in the EN 18031 series, developed for RED compliance, align closely with the CRA’s cybersecurity baseline. A manufacturer whose modules hold current EN 18031 certifications can build on an established security foundation and address EU CRA requirements through incremental extensions rather than a full redesign.

Manufacturers whose products lack RED cybersecurity certification may require a broader initial effort to establish their technical security baseline and supporting processes, along with the necessary documentation, resulting in a broader initial compliance effort.

Wireless connectivity is a potential attack surface in connected products. Wireless modules directly influence how a product handles secure communication and authentication. They also affect remote update capabilities over cellular networks and introduce dependencies on software components and external services that manufacturers must manage under the regulation’s requirements.

While IoT device manufacturers make integration and configuration decisions at the final product level, module-level security features contribute directly to CRA compliance.

Telit Cinterion has certified its products under the EN 18031 standards for RED compliance. Our modules include security features such as remote firmware update mechanisms. These allow customers to address security issues and deploy patches over the product lifecycle, consistent with the CRA’s requirements for security updates and resilience.

We also maintain a dedicated Product Security Incident Response Team (PSIRT), along with technical support channels that serve as the primary entry point for reporting potential security issues.

Class (B2B/B2C)
Ignore
Ingest Status
Need Review
Dedupe hash
ce5a6ca8390fdba062867b364fa90482
Press Eligible
No
Press Eligible Reason
Irrelevant (need review): Provides IoT manufacturers with business-focused guidance on cybersecurity compliance requirements and deadlines.
Source Name
Telit Cinterion
Original Summary

<p>The European Union (EU) Cyber Resilience Act (CRA) establishes mandatory cybersecurity requirements for products with digital elements placed on the European market. The regulation applies general requirements across all products, with more specific obligations for selected product categories. For companies building connected products, this is a fundamental shift. Manufacturers must build cybersecurity into their products...</p>
<p>The post <a href="https://www.telit.com/blog/cyber-resilience-act-iot-compliance/">Cyber Resilience Act: What IoT Manufacturers Need to Know</a> appeared first on <a href="https://www.telit.com">Telit Cinterion</a>.</p>

Image URL
https://www.telit.com/wp-content/uploads/2026/06/CRA_1.jpg
Source Node
Content Hash (SHA-256, erste 32 hex)
29cc362dcc0b64bca07e1f279430adb8
Critical IoT Solutions: Always-On IoT Connectivity
Image File
Original HTML

Connectivity

Critical IoT Solutions: Always-On IoT Connectivity

By Noam Shany

June 23, 2026

Estimated reading time: 5 minutes

Mission-critical Internet of Things (IoT) solutions are connected systems in which a loss of connectivity poses unacceptable operational risk. A deployment is mission-critical when downtime significantly disrupts operations that depend on devices remaining reachable to support:

In these deployments, downtime is not just inconvenient. It can delay emergency response and disrupt revenue-critical transactions. A mission-critical solution depends on resilience and an uptime strategy that can withstand predictable failure points.

A critical IoT solution depends on more than the device. It also depends on the connectivity architecture that keeps the device reachable, even when network conditions change.

Many of these deployments support time-sensitive operations. Even a brief connectivity loss can create immediate operational issues. Always-on connectivity is vital for these applications, which can include:

For use cases such as these, uptime is a design requirement.

Many always-on failures start with the assumption that one network is enough. A single mobile network operator (MNO) can be a solid choice in a stable footprint. However, it is not a redundancy strategy.

A critical IoT solution deployed outside its home market can lose connectivity during a core network outage if it depends on a single MNO. Devices may remain offline until the operator recovers. A commercial dispute can cause a disruption if service terms change or access is restricted.

Geography introduces additional risk. A carrier in a market with national roaming restrictions may be unable to support a redundancy model beyond its own network. When a deployment crosses borders, a connectivity plan that works in one country can degrade in another.

Coverage and policy constraints vary by country. Critical IoT deployments require a design that accounts for scenarios that can disrupt service, such as cross-border constraints or network outages. That typically involves an alternate connectivity path that is not tied to a single operator.

Today, a traditional roaming solution is often not enough. A multi-IMSI solution that relies on roaming across multiple service layers and partners still has inherent weak points.

A core network failure, whether on the mobile virtual network operator (MVNO) side or within one of the primary connectivity partners, can trigger a chain of events that ultimately leads to service outages.

In critical asset monitoring, for example, a core network failure can result in the temporary loss of real‑time location visibility. This impacts logistics planning and breaches SLA commitments. In some cases, it may even lead to regulatory compliance issues and financial penalties.

This is where an IoT MVNO with deep expertise and control over its infrastructure at both the eSIM profile and core network levels becomes essential. Independent eSIM profiles connect to separate core networks and partner ecosystems. Intelligent software at the device edge manages these scenarios to support true multinetwork access. The result is a significant reduction in downtime when network availability changes, helping maintain service continuity for critical IoT applications.

Global roaming allows devices to connect to visited networks outside an operator’s home country. This simplifies early IoT deployments by supporting rollouts across countries without requiring region‑specific hardware variants.

For use cases that span multiple geographies or need basic network flexibility, global roaming remains a practical and widely adopted approach.

Embedded Universal Integrated Circuit Card (eUICC) technology builds on that foundation. It lets organizations remotely provision operator profiles and switch between them, improving operational flexibility across regions.

When permanent roaming restrictions apply, organizations can remotely install a local operator profile to remain compliant without a physical SIM swap. This capability is particularly valuable for manufacturers that design devices to operate across multiple markets over long lifecycles.

However, while multi-IMSI or eUICC‑based roaming approaches increase network choice, they do not eliminate every point of failure. Profiles still rely on shared service layers or common core network infrastructure. If a core‑level outage occurs, it can affect all available IMSIs simultaneously, limiting resilience during major service disruptions.

eSIM Protect goes beyond traditional roaming and profile management by introducing true redundancy. It uses independent eSIM profiles connected to separate core networks and partner ecosystems, intelligently managed to safeguard uptime for critical IoT deployments.

Critical IoT deployments need connectivity that stays online as network conditions shift. Telit Cinterion helps you build a global strategy that prioritizes uptime. We provide true global reach with resilient, always-on connectivity.

Contact us to future-proof your mission-critical global IoT deployments.

Editor’s note: This blog was originally published on 15 August 2023 and has since been updated.

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
b99ba57150612eed8c24e8127fd21953
Press Eligible
Yes
Press Eligible Reason
Manuelle Prüfung nötig. Risiko: MEDIUM. Flags: ['none']. Stichprobe: False
Source Name
Telit Cinterion
Original Summary

<p>Mission-critical Internet of Things (IoT) solutions are connected systems in which a loss of connectivity poses unacceptable operational risk. A deployment is mission-critical when downtime significantly disrupts operations that depend on devices remaining reachable to support: In these deployments, downtime is not just inconvenient. It can delay emergency response and disrupt revenue-critical transactions. A mission-critical...</p>
<p>The post <a href="https://www.telit.com/blog/mission-critical-solutions-importance/">Crit… IoT Solutions: Always-On IoT Connectivity</a> appeared first on <a href="https://www.telit.com">Telit Cinterion</a>.</p>

Image URL
https://www.telit.com/wp-content/uploads/2023/08/critical_iot_1.jpg
Source Node
Content Hash (SHA-256, erste 32 hex)
185448f8366f83eeed1820154042068c
Inside Telit Cinterion’s IoT R&D Process
Image File
Original HTML

Solutions

Inside Telit Cinterion’s IoT R&D Process

July 8, 2026

Estimated reading time: 10 minutes

Telit Cinterion’s Internet of Things (IoT) R&D team develops connected products and devices for companies at every stage of development. Some customers arrive with a product concept and a target market. Others have a device that needs connectivity added, or a cellular product approaching end of life that needs to migrate to a newer network generation.

Wherever a project starts, the requirements are the same. A connected product only works when hardware, firmware, and wireless connectivity perform together across every region the device operates in.

Connected products rarely fail in one place; they fail at the seams between those layers. When separate companies each build a piece, no one owns the whole picture. Firmware doesn’t match the hardware. RF performance may not be tested in regions where the product will ship.

Telit Cinterion’s IoT product development process closes those gaps before they become field failures.

Telit Cinterion runs IoT R&D centers in the U.S., Italy, Korea, and India, keeping technical expertise close to the markets customers sell into. The global research and development teams operate as one across time zones and disciplines, covering:

One team owns the product at every stage. A four-phase development process sets clear expectations for what the customer provides and what the R&D team delivers at each stage.

While not every IoT project needs every discipline, the full bench is there:

A security architect is always assigned to the project. RF expertise is also a constant; it’s the most critical part of almost any IoT product.

Because the same core IoT R&D team stays with a project from feasibility through mass production, the engineers who built the product are the ones who diagnose any issue that may surface after launch.

Throughout the development cycle, a dedicated Telit Cinterion contact provides regular status updates, and customers can reach the R&D team if they have questions.

Telit Cinterion’s customer support team collects the full set of product requirements from the customer. Product management then refines those requirements with the customer before the R&D team begins the feasibility assessment.

Two inputs shape the project.

The first is a clear, well-negotiated set of product requirements. When specs are ambiguous, the cost shows up later as rework, iteration cycles, and sometimes a full design restart.

The second is the end use case. Knowing how the connected device will operate in the field lets the R&D team focus development and testing on the conditions that matter.

A checklist of what to have ready before starting the development process. Get My R&D Checklist

Much of R&D starts with technology, not a specific customer. Telit Cinterion’s R&D team builds IoT platforms around each new generation of cellular technology and each chipset advancement, anticipating where the market is heading.

These platforms become portfolio products, the standard modules and solutions any customer can buy. Because they’re general-purpose, testing aims to cover the broadest possible range of operating scenarios.

About 50% to 60% of projects are custom IoT solutions built for specific deployment requirements. These solutions range from software modifications to full hardware redesigns.

Customization works a little like the auto industry. You build a standard model, then a customer wants a specific color, a heavier wire gauge, or a different engine because they’re racing.

Larger enterprises typically engage the R&D team for that deployment-specific work.

Roughly 80% of customizations are software:

Hardware changes account for the other 20%.

For smaller businesses, a standard portfolio product usually matches their needs without custom development.

The IoT R&D team has developed products across a range of industries:

Roughly 90% of solution products include a Telit Cinterion module. About 40% use NExT™ connectivity services, and another 40% run on the deviceWISE® platform.

Once requirements are set, development moves through four phases.

Engineering Validation Test

Design Validation Test

Production Validation Test

One R&D team owns the product from feasibility through mass production.

The IoT R&D team spends significant time in this phase:

Because the products are general-purpose platforms used across many applications, the security review must anticipate a wide range of deployment scenarios up front.

Cellular products also need ongoing software and firmware updates to stay secure and stable as network requirements change. Knowing that those updates will be required for years after launch shapes design and testing from the start.

The team runs design reviews before prototyping, bringing R&D engineers and technical support together to catch design problems early. Product management reviews the assessment and negotiates terms with the customer. Once approved, the project moves into execution.

In the current supply chain environment, a single PCB fabrication cycle can take months. Prototype fabrication can account for half of the total development timeline. That is why the team would rather spend two extra weeks getting the first prototype right than wait months for a second PCB spin. Telit Cinterion averages 1.8 prototype iterations per project; most products reach mass production after one or two.

The first working prototype. Hardware and software are both preliminary. Main features are in, but some components and performance may not yet meet the full requirements. Customers can begin early evaluation of the product, but EVT samples shouldn’t be used for final application design, performance testing, or certification.

Hardware is stable. Software is still preliminary, with additional features added but not yet final. Customers can use DVT samples for hardware application design and initial performance testing. DVT is also when product certification and new product introduction production can begin.

DVT-stage designs are built in a small series on the final production plant’s assembly and test lines, the same ones that will be used for mass production. The product has received all required regulatory and carrier certifications for its target region. The customer approves the final design, and manufacturing begins.

Once software is ready, the team runs endurance testing and security testing to verify stability and identify vulnerabilities before the product moves forward.

Telit Cinterion’s anechoic chambers at the Trieste, Italy, facility are purpose-built for multiple cellular technologies. The RF team tests every frequency combination a product might encounter in deployment and confirms performance across all of them. This is not a formality. The team has seen customer IoT devices that were effectively blind in certain frequency bands and couldn’t connect in parts of the U.S. For a tracking device, that’s a nightmare, and it’s exactly what this testing prevents.

Products are tested against real-world operating conditions:

For modules and select solution products, the IoT R&D team deploys devices across multiple countries, testing with different operators and cross-border roaming scenarios to confirm connectivity in the field.

Before mass production, the team validates the manufacturing process, including reflow process analysis with X-ray verification to confirm solder joint reliability for BGA modules on the application PCB. Every module is tested and calibrated before it leaves production.

Every Telit Cinterion product needs regulatory and carrier certification before it can ship. This is handled in-house by the Global Certification team, with application-level precertification testing to expose issues before formal certification cycles begin.

Certification timelines vary by target region, and newer technology increases complexity. Products targeting multiple regions carry a proportionally larger certification workload.

R&D support continues past production. The team:

More often than not, an issue traces back to configuration or usage rather than a product defect, and the team helps the customer find and fix the source of the problem.

If a device fails in the field, Telit Cinterion runs a Return Merchandise Authorization (RMA) analysis to determine whether the root cause is the product design or how the device was used. Support continues until the product reaches stable operation.

Any company bringing a connected product to market needs to decide how much of the development lifecycle to manage internally. Telit Cinterion’s IoT product engineering and R&D services are built to carry the rest. The team that evaluates feasibility is the same team that:

Because the module, connectivity, and platform come from one organization, R&D has end-to-end visibility into how each layer interacts. If an issue arises, there is one point of accountability.

Ready to start the R&D process? Get in touch

Who owns the IP when outsourcing IoT product development?

IP for Telit Cinterion’s own modules stays with Telit Cinterion. For custom solution products, ownership is negotiated on a per-project basis. Some customers fund the development costs directly and retain full IP rights, while others leave ownership with Telit Cinterion.

When does it make sense to use an IoT R&D partner instead of building in-house?

When a company has a clear vision for a connected product and an existing customer base, but lacks the in-house engineering capacity to develop the device on its own. The company brings the concept and market knowledge. Telit Cinterion brings the IoT product development expertise to deliver a certified, production-ready device.

Companies that don’t need a fully custom IoT solution can also work with Telit Cinterion’s existing portfolio. In many cases, a standard product meets their requirements without customization.
Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
0dc29a217f3abf3ca8017b644e2ad93a
Press Eligible
Yes
Press Eligible Reason
Manuelle Prüfung nötig. Risiko: MEDIUM. Flags: ['numbers']. Stichprobe: False
Source Name
Telit Cinterion
Original Summary

<p>Telit Cinterion’s Internet of Things (IoT) R&#38;D team develops connected products and devices for companies at every stage of development. Some customers arrive with a product concept and a target market. Others have a device that needs connectivity added, or a cellular product approaching end of life that needs to migrate to a newer network...</p>
<p>The post <a href="https://www.telit.com/blog/inside-telit-cinterions-iot-r-and-d-process/… Telit Cinterion&#8217;s IoT R&amp;D Process </a> appeared first on <a href="https://www.telit.com">Telit Cinterion</a>.</p>

Image URL
https://www.telit.com/wp-content/uploads/2026/07/RD_process_1.jpg
Source Node
Content Hash (SHA-256, erste 32 hex)
824c1ea85a58440da284967cd8ab5780
CRA Vulnerability Reporting: What IoT Manufacturers Need to Know Before September 2026
Image File
Original HTML

Modules

CRA Vulnerability Reporting: What IoT Manufacturers Need to Know Before September 2026

By Enrico Milanese

Federico Della Valle

July 21, 2026

Estimated reading time: 12 minutes

The first EU Cyber Resilience Act (CRA) vulnerability reporting obligations begin on September 11, 2026. On that date, manufacturers of products with digital elements on the EU market must report actively exploited vulnerabilities and severe security incidents to EU authorities.

This reporting mandate falls under Article 14 of the CRA. It is separate from the product-level cybersecurity requirements under Article 13, which do not apply until December 11, 2027.

For an overview of the full Cyber Resilience Act, see our EU Cyber Resilience Act blog.

Two separate categories of events require reporting under Article 14: actively exploited vulnerabilities and severe security incidents. Each has its own trigger and timeline.

A manufacturer must report to the European Union Agency for Cybersecurity (ENISA) when reliable evidence confirms that a malicious actor has exploited a vulnerability in a product. This does not include authorized activities such as penetration testing and bug bounty programs.

Confirmed active exploitation triggers the reporting obligation. A published Common Vulnerabilities and Exposures (CVE) entry or the existence of a theoretical risk does not.

Awareness of active exploitation may come through multiple channels:

Manufacturers must also report severe incidents that affect product security. This includes incidents that negatively affect or could negatively affect the availability, authenticity, integrity, or confidentiality of data or functions.

The incident must compromise the security of the product or the processes used to develop, produce, or maintain it. For example, if an attacker breaches the public key infrastructure (PKI) used to authenticate devices during manufacturing, that qualifies as a severe security incident.

Manufacturers submit reports through ENISA’s Single Reporting Platform (SRP). The platform routes each notification to the national Computer Security Incident Response Team (CSIRT) in the manufacturer’s Member State of establishment. It will simultaneously make the report accessible to ENISA. Manufacturers notify once; the platform handles distribution.

The SRP is expected to be operational by September 11, 2026, following a pre-launch testing period. ENISA has published an FAQ on the SRP explaining the information manufacturers must provide when submitting a report. Details are listed under the FAQ “What information must be included in the report?”

Application Programming Interfaces (APIs) are not expected to be included in the first SRP release. Automated report submission via API will not be supported.

Manufacturers with an existing incident response plan will almost certainly need to revise it to meet the requirements of Article 14 of the CRA. Particular attention should be given to reporting workflows and timelines, taking into account the obligations under other applicable rules (e.g., EU 2022/2555 NIS2, GDPR) or sector-specific reporting regimes.

As part of the European Commission’s objective to simplify the EU New Legislative Framework through digital tools, the Commission published proposal 2025/0360. The proposal aims to make ENISA’s SRP the common portal for reporting obligations under several EU rules.

For manufacturers based outside the EU, the coordinator CSIRT is determined by the Member State of the entity responsible for placing the product on the EU market. This may be:

Non-EU manufacturers should identify which entity places their product on the EU market and confirm the corresponding Member State CSIRT before September 2026. The receiving CSIRT shares each notification with CSIRTs in all Member States where the product has been made available. Manufacturers can request a delay if premature dissemination could increase exploitation risk, such as while a patch is in development (Commission Delegated Regulation (EU) 2026/881).

Article 14(8) also requires manufacturers to notify affected users of the vulnerability or incident, and of any corrective measures, without undue delay. The CRA uses the phrase “where appropriate.” Unless a manufacturer can definitively confirm that only a specific subset of users is impacted, notification should extend to all users of the product.

If a manufacturer does not do so in a timely manner, the receiving CSIRT may notify users directly.

Both reporting tracks follow a staged notification process, but the final report deadlines differ.

The 24-hour clock starts when the manufacturer becomes aware of the active exploitation or severe incident, not when the CVE was first published or when the vulnerability was first discovered.

Reporting obligations are not limited to new products. Under Article 69(3), they apply to all products with digital elements on the EU market, regardless of when they were placed on the market. For example, a device sold in 2023 is in scope starting September 2026.

However, for legacy products, complete software inventories may not exist. Original tooling or build environments may no longer be available. Therefore, other CRA obligations, such as vulnerability handling under Article 13, do not extend to preexisting products.

Need help assessing your existing product portfolio for CRA scope? Talk to our team.

The CRA imposes reporting obligations on the manufacturer, defined as the entity placing the product on the EU market. Meeting a CRA 24-hour notification window requires visibility into every software component in the product, including:

A complete and current software bill of materials (SBOM) for each product in scope is the operational prerequisite for determining whether a newly disclosed vulnerability affects that product.

While the legal obligation belongs to the manufacturer, the operational requirements extend to the supply chain. Companies that supply components rather than finished products should expect their customers to require transparency into:

Without that information from suppliers, manufacturers cannot assess whether a disclosed vulnerability affects their products.

The following measures are operationally necessary to meet the September 2026 CRA vulnerability reporting deadline. Some (such as SBOM maintenance and CVD policies) are not legally required until December 2027 under Article 13.

Manufacturers should establish a process to manage SBOMs for all in-scope products in a machine-readable format (e.g., CycloneDX or SPDX). This includes products already on the EU market, not just those in development.

For legacy products where build-time SBOMs do not exist, software composition analysis (SCA) tooling can support this process, scanning current firmware images to generate a baseline.

An SBOM is the starting point. It shows which software components are inside a product. This visibility is essential for understanding potential exposure.

But an SBOM alone cannot provide insights into potential cyber risk. It does not show whether a vulnerability can be exploited in the final product’s specific configuration or whether the vulnerability matters in practice.

This is where Vulnerability Exploitability eXchange (VEX) becomes valuable. VEX adds the missing context and answers the real questions: Does this CVE affect my product? Is it irrelevant? Under review? Already fixed?

Together, they turn software transparency into actionable vulnerability triage and clearer risk visibility.

A continuous process should match disclosed vulnerabilities against SBOM component inventories. Manufacturers could monitor:

Security automation processes support a risk-based vulnerability management approach. They help teams correlate vulnerability sources with product data, assess potential product impact, and retain evidence of triage decisions.

This approach improves collaboration between security and engineering teams. It supports company readiness for CRA vulnerability handling and reporting obligations.

ENISA’s SRP will be operational by September 2026. Before that date, manufacturers should define internal policies and procedures, as well as a responsibility matrix for escalation paths.

This process is usually cross-functional. The exact teams involved will depend on the company’s size, product complexity, and internal structure. Groups that may participate include:

Aligning all relevant internal stakeholders ensures that technical analysis, regulatory assessment, customer impact, and internal approval receive proper coverage when reporting timelines are tight.

Each reporting stage needs a short runbook in checklist format that should specify:

These should be concise, actionable documents rather than high-level policy statements.

Prepare for CRA Vulnerability Reporting

Before September 2026, manufacturers should run at least one tabletop exercise simulating the full reporting chain:

The CRA requires a published CVD policy by December 2027 (Article 13). Establishing one ahead of the reporting deadline provides the intake channel needed to receive external reports of exploitation.

A practical CVD process should describe how external vulnerability reports are:

Companies do not need to design their vulnerability intake and handling process from scratch. Standards and guidance offering useful starting points include:

The intake process should connect to the internal triage workflow so that a report of active exploitation immediately starts the 24-hour reporting clock.

For products that include third-party components, meeting the 24-hour reporting window depends in part on supplier responsiveness. Manufacturers should confirm that each supplier can provide:

Where these commitments do not exist, manufacturers should negotiate them into supplier agreements.

ENISA’s FAQ confirms that manufacturers must register before submitting reports through the SRP.

Class (B2B/B2C)
B2B
Ingest Status
Need Review
Dedupe hash
77cf2e348377388c3d4e3ac27f5e0adb
Press Eligible
Yes
Press Eligible Reason
QA FAIL (need review): Factual/date error: the target states the reporting obligation begins 'more than 15 months' before the Article 13 deadline, but the source dates are exactly 15 months apart (September 11, 2026 to December 11, 2027). This incorrect comparative number is not supported by the source.
Source Name
Telit Cinterion
Original Summary

<p>The first EU Cyber Resilience Act (CRA) vulnerability reporting obligations begin on September 11, 2026. On that date, manufacturers of products with digital elements on the EU market must report actively exploited vulnerabilities and severe security incidents to EU authorities. This reporting mandate falls under Article 14 of the CRA. It is separate from the...</p>
<p>The post <a href="https://www.telit.com/blog/cra-vulnerability-reporting-september-2026/"… Vulnerability Reporting: What IoT Manufacturers Need to Know Before September 2026</a> appeared first on <a href="https://www.telit.com">Telit Cinterion</a>.</p>

Image URL
https://www.telit.com/wp-content/uploads/2026/07/CRA_reporting_8.jpg
Source Node
Generated Article_json
{"target_audience": "b2b", "is_medical": false, "ai_generated_title": "CRA Reporting Duties Hit IoT Makers on September 11, 2026", "body_html": "<p><strong>European Union -- [CURRENT_DATE] --</strong> Manufacturers of products with digital elements sold in the EU must report actively exploited vulnerabilities and severe security incidents from September 11, 2026, more than 15 months before the Cyber Resilience Act's (CRA) product-level security requirements apply on December 11, 2027.</p><h5>Article 14 reporting starts 15 months ahead of Article 13 product rules</h5><p>The reporting mandate sits in Article 14 of the CRA and is separate from the Article 13 requirements. Two event categories trigger it: actively exploited vulnerabilities and severe security incidents. Each has its own trigger and timeline, and the staged notification process ends in different final-report deadlines.</p><p>An exploited vulnerability becomes reportable once reliable evidence confirms a malicious actor has used it. A published CVE entry or a theoretical risk does not trigger the duty. Authorized activity such as penetration testing and bug bounty programs is excluded. A severe incident is one that negatively affects, or could affect, the availability, authenticity, integrity or confidentiality of data or functions. A breach of the public key infrastructure used to authenticate devices during manufacturing is one example.</p><p>The 24-hour clock starts when the manufacturer becomes aware of the exploitation or incident. Neither CVE publication nor first discovery of the flaw starts it.</p><h5>ENISA's Single Reporting Platform routes each report to one national CSIRT</h5><p>Reports go through the Single Reporting Platform (SRP) of the European Union Agency for Cybersecurity (ENISA). The platform sends each notification to the national CSIRT of the manufacturer's Member State of establishment and makes it accessible to ENISA at the same time. Manufacturers must register before submitting. The SRP is expected to be operational by September 11, 2026, after a pre-launch testing period. The first release will have no API, so automated submission will not be supported.</p><p>For non-EU manufacturers, the coordinating CSIRT is determined by the Member State of the entity that places the product on the EU market. The receiving CSIRT shares each notification with CSIRTs in all Member States where the product is available. Manufacturers can request a delay if early dissemination could raise exploitation risk, for example while a patch is in development, under Commission Delegated Regulation (EU) 2026/881.</p><p>Article 14(8) also requires manufacturers to notify affected users without undue delay. Unless a manufacturer can confirm that only a subset of users is affected, notification should reach all users. If the manufacturer fails to act in time, the receiving CSIRT may notify users directly.</p><h5>Legacy products sold before 2026 fall inside the reporting scope</h5><p>Under Article 69(3), reporting duties cover all products with digital elements on the EU market, whenever they were placed there. A device sold in 2023 is in scope from September 2026. Other CRA obligations, such as Article 13 vulnerability handling, do not extend to preexisting products.</p><p>Many legacy products lack complete software inventories, and original build environments may no longer exist. For these, software composition analysis tooling can scan current firmware images to generate a baseline software bill of materials (SBOM).</p><h5>Software bills of materials and supplier data determine whether the 24-hour window is achievable</h5><p>A complete, current SBOM in a machine-readable format such as CycloneDX or SPDX is the operational prerequisite for judging whether a new vulnerability affects a product. Vulnerability Exploitability eXchange (VEX) data adds context on whether a CVE is affecting, irrelevant, under review or already fixed.</p><p>Manufacturers that incorporate third-party components depend on supplier responsiveness to meet the deadline. Where suppliers have made no commitments, manufacturers should negotiate them into supply agreements. Existing incident response plans will almost certainly need revision. They must account for parallel obligations under NIS2 (EU 2022/2555), GDPR and sector-specific regimes.</p><p>Manufacturers should define escalation responsibilities across teams and write short checklist runbooks for each reporting stage. They should also run at least one tabletop exercise of the full reporting chain before September 2026. A coordinated vulnerability disclosure (CVD) policy is legally required only by December 2027, but publishing one earlier creates the intake channel for external exploitation reports. That channel should feed the internal triage workflow so a report of active exploitation starts the 24-hour clock immediately.</p><p>The European Commission's proposal 2025/0360 would make the SRP the common portal for reporting obligations under several EU rules.</p>", "meta_description": "EU Cyber Resilience Act reporting starts September 11, 2026: 24-hour clocks, ENISA's Single Reporting Platform, legacy product scope and SBOM readiness for IoT makers.", "seo_keywords": "Cyber Resilience Act, CRA Article 14, vulnerability reporting, ENISA Single Reporting Platform, IoT manufacturers, SBOM, VEX, September 2026, EU cybersecurity compliance", "companies": [], "industries": ["Electronics Manufacturing"], "markets_regions": ["European Union", "Europe"], "news_type": ["regulatory_update"], "products": ["ENISA Single Reporting Platform"], "themes": ["regulatory_compliance", "cybersecurity", "supply_chain"], "events": [], "cta_text": "Assess your product portfolio's CRA scope and reporting readiness ahead of the September 11, 2026 start date", "learn_more": "", "fact_check": {"accuracy_score": 100, "legal_risk": "low", "corrections_made": ["Source city not stated; region 'European Union' used in dateline", "Final-report deadlines omitted because the source does not state them"], "recommendation": "publish"}}
Content Hash (SHA-256, erste 32 hex)
fbf984979fd563453308db125bf4fd30
Q&A: How AI Updates Telit Cinterion’s IoT Product Development
Image File
Original HTML

Solutions

Q&A: How AI Updates Telit Cinterion’s IoT Product Development

July 23, 2026

Estimated reading time: 6 minutes

Internet of Things (IoT) product development is entering a new stage as artificial intelligence (AI) becomes part of daily engineering tasks. More teams are integrating AI into their processes, using it as a practical tool rather than experimental technology.

Antonino Sgroi, Telit Cinterion’s global head of R&D, discusses how his teams incorporate AI across the IoT product development process and why the implementation sequence matters.

Telit Cinterion’s R&D process supports the entire product lifecycle. Quality discipline is an integral part of how that system operates and is built into each development phase.

We follow rigorous development standards across our global operations. Validation testing is a crucial step, not just a formality. We conduct design reviews with technical support and R&D engineers and perform application-level precertification testing.

Go Behind the Scenes

See how Telit Cinterion’s R&D team takes an IoT product from concept to certified hardware. Read Inside Telit Cinterion’s IoT R&D Process

New ideas tend to arrive with noise and skepticism. They create uncertainty, but also enthusiasm and attention. Over time, they become the foundation of how teams build and deliver technology. What starts as disruption becomes a normal part of the toolbox.

AI is not just an engineering tool. It must support the entire system, or it simply shifts the bottleneck elsewhere. Today, it is over-discussed, almost mythologized. But before long, I expect it to become a silent and powerful companion in our work, like other waves of innovation I have seen over the last 20 years.

My motivation to introduce AI into our development cycle was practical. Our engineers are exceptional, but too much of their time is spent on repetitive, low-value work. AI lets us remove that friction so they can focus on the architecture and innovation that matter most to our customers.

AI is powerful and streamlines processes when used correctly. We use it to eliminate friction, allowing teams to focus on the architecture and innovation that matter most. With AI, we create more space for innovation that provides value to customers.

We followed a precise sequence because with AI, where you start is as important as how you start.

We began here on purpose because accelerating development without strengthening validation just moves the bottleneck downstream. We used AI to speed up log analysis and root-cause detection, so validation could keep pace once everything else got faster.

That foundation was important because the rest of the cycle was about to accelerate. It positioned validation to scale with that speed instead of becoming the next bottleneck.

Only once validation was ready did we expand AI into software development, where it now generates repetitive code and speeds up reviews without lowering our quality bar. We also use it for guided debugging and to draft documentation where appropriate.

This is also where a broader strategy comes in. We invest in customized software and embedded algorithms that make development easier for our customers, so they can move from concept to product more efficiently.

This improves throughput without compromising quality because validation has already been reinforced.

From there, we brought AI into customer support, which is often the first to spot patterns in the field. AI helps us interpret logs faster and surface recurring issues, so support engineers reach recommendations sooner. Those insights feed back into engineering.

Strengthening support strengthened the whole pipeline. If we had accelerated coding first, everything else would have collapsed.

We are still searching for the right AI solutions for hardware. AI could help significantly with PCB layout and RF tuning, and eventually with digital twin simulation that tests assumptions before we commit to a build. That can improve early feasibility decisions and reduce avoidable rework.

The tools are not yet mature enough for our industrial standards, and we will not lower that bar. Still, I am convinced the breakthrough is coming, and when it does, we will integrate it quickly.

The 2026 hackathon was our cultural accelerator. The idea came from engineers across different regions, which makes it a strong example of bottom-up innovation.

Engineers needed protected time to experiment with AI freely, with no pressure and no deadlines.

The goal was not about finding the single “best idea.” I hoped to spark curiosity and build the confidence to experiment and to get people to exchange ideas across regions. After the event, people stopped asking why AI and started asking where else we can apply it. We are already planning another for 2027.

Two things stand out: execution speed, because teams solve problems faster and deliver sooner, and a mindset shift. Engineers now naturally ask whether AI can help them do something smarter. That shift is worth more than any single tool.

Several directions, and they all point the same way. Development and intelligence are moving closer together.

We are watching multi-agent workflows and AI-assisted hardware design most closely, with testing pipelines and edge intelligence growing more adaptive over time. They can change how teams organize complex work: instead of one engineer driving a task end to end, AI agents can help break work into smaller steps. Those steps move forward in parallel with human oversight.

We are also tracking AI-assisted RF and hardware design, even if the tools still need time to mature for industrial use. On the software side, we expect testing pipelines to become more adaptive as AI improves signal detection.

Over time, we also see deeper edge intelligence emerging as more products require local decision-making, not just connectivity. The boundary between development and intelligence is shrinking quickly.

Start small but make the wins visible. Momentum matters, especially when teams are skeptical.

Make sure teams understand how to use AI in IoT product development, or it becomes noise instead of leverage. Build governance and internal champions early, and stay adaptable, because AI evolves constantly. Above all, AI does not replace engineers; it amplifies engineers.

We are actively exploring what it means to embed AI in our products. We will share more when we are ready.

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
72bf5f7572ef9de5ae08127de4c79906
Press Eligible
Yes
Press Eligible Reason
Manuelle Prüfung nötig. Risiko: LOW. Flags: ['none']. Stichprobe: True
Source Name
Telit Cinterion
Original Summary

<p>Internet of Things (IoT) product development is entering a new stage as artificial intelligence (AI) becomes part of daily engineering tasks. More teams are integrating AI into their processes, using it as a practical tool rather than experimental technology. &#160; Antonino Sgroi, Telit Cinterion&#8217;s global head of R&#38;D, discusses how his teams incorporate AI across...</p>
<p>The post <a href="https://www.telit.com/blog/qa-ai-in-iot-product-development/">Q&amp;A: How AI Updates Telit Cinterion&#8217;s IoT Product Development</a> appeared first on <a href="https://www.telit.com">Telit Cinterion</a>.</p>

Image URL
https://www.telit.com/wp-content/uploads/2026/07/AI_product_dev_1.jpg
Source Node
Content Hash (SHA-256, erste 32 hex)
876dd89a2234cf1bced84e8a4d1de02e
Q&A: IoT Product Development with Telit Cinterion
Image File
Original HTML

Solutions

Q&A: IoT Product Development with Telit Cinterion

August 12, 2026

Estimated reading time: 4 minutes

When planning an IoT product, choosing between in-house development and a partner is an early key decision.

Antonino Sgroi, Telit Cinterion’s global head of R&D, explains what partnership with the IoT R&D team looks like and how it lowers costs and risk when bringing a connected device to market.

A company with a clear idea and a customer base that does not have the in-house engineering capacity or the appetite to invest in building the device itself.

You bring the vision and the market knowledge. We provide cellular and connectivity expertise, along with platforms, to develop that idea into a finished, certified product, so you can stay focused on your business.

One team owns your product from feasibility through mass production. The engineers who design it are the same ones who support it after launch. You’ll have a dedicated contact who keeps you updated, and you can reach the team whenever you have a question. We follow a structured four-phase process to get there.

For the full step-by-step walkthrough, see Inside Telit Cinterion’s IoT R&D Process.

First, we spend real time up front so the first prototype is right. We average under two per project.

Second, and this is something I think is important, we invest in customized software and embedded algorithms that make development easier for the customer. The goal is to take complexity off your plate so you move from concept to product faster.

On top of that, we validate and certify in-house, so problems surface in our labs instead of in your field deployment.

A design house delivers a design and then leaves the rest to you. You own production and certification, and you handle field support yourself. An ODM is focused on manufacturing and may skip the detailed RF and field validation a connected product needs.

We do it all, and we stand behind the product. We act more as a partner than as a vendor.

For our own modules, the IP stays with Telit Cinterion. For a custom solution product, it depends on the project.

Some customers fund the development and keep full IP rights. Others prefer to leave ownership with us. There is no single rule. We work it out per project.

A wide range, including:

The environments differ, but the goal does not. Each custom IoT solution has to be a stable, validated product that the customer can build on.

An IoT product development partner performs the technical work and certification required to turn an idea into a finished connected product. Telit Cinterion’s IoT product engineering and R&D services do exactly that.

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
5edde407fcfad5ff085fd2368ac8a712
Press Eligible
Yes
Press Eligible Reason
IoT product development and R&D services for businesses.
Source Name
Telit Cinterion
Original Summary

<p>When planning an IoT product, choosing between in-house development and a partner is an early key decision. Antonino Sgroi, Telit Cinterion&#8217;s global head of R&#38;D, explains what partnership with the IoT R&#38;D team looks like and how it lowers costs and risk when bringing a connected device to market. Who should&#160;bring in&#160;a&#160;product development partner instead of building in-house?&#160; A&#160;company&#160;with&#160;a clear idea and a customer base&#160;that&#160;does not have the in-house...</p>
<p>The post <a href="https://www.telit.com/blog/rd-qa-iot-product-development-partner/">Q&am… IoT Product Development with Telit Cinterion </a> appeared first on <a href="https://www.telit.com">Telit Cinterion</a>.</p>

Image URL
https://www.telit.com/wp-content/uploads/2026/08/IoT_RD.jpg
Source Node
Content Hash (SHA-256, erste 32 hex)
cc539dc106313b71ff4c52a068f839cf