The Proof Is In the Platform: Why Modern GRC Teams Choose Hyperproof Over Trackers
Image File
Original HTML

The Proof Is In the Platform: Why Modern GRC Teams Choose Hyperproof Over Trackers

Most GRC platforms were built as trackers, not operational systems. They log that work happened without doing anything to reduce the manual burden. Teams re-map the same controls every time a new framework enters scope, coordinate audit prep by hand across siloed departments, and get stuck flat-structuring compliance for an enterprise that’s anything but flat.

Meanwhile, “AI-powered” and “intuitive” have become generic buzzwords, leaving buyers to discern true technical capability from a marketing message.

Look beyond the claims for the proof. With Hyperproof, the proof is in the platform.

The industry’s largest framework library and 200+ integrations

Hyperproof features the largest pre-built framework library on the market, enabling teams to map once and reuse evidence everywhere instead of starting from scratch.

Through the Hyperproof Crosswalk and Jumpstart capabilities, requirements from our 160+ framework programs are mapped across nearly 2,500 domains. You can use any existing program framework to jumpstart coverage for new frameworks — delivering complete common control coverage across your entire program.

Our framework library is complemented by Hyperproof’s 200+ integration library, which collects evidence on demand or on a scheduled cadence from your cloud storage, SIEM, and ITSM platforms. These integrations work natively with your task management tools to streamline your workflows and keep teams working where they already live.

The Impact: 70% increase in compliance productivity. 66% reduction in duplicative controls. 350 hours saved on audit prep per year.

Appian uses Hyperproof to streamline GRC for 28 frameworks. Read the case study.

A GRC workflow engine that actually orchestrates the work

Hyperproof’s workflow engine orchestrates your compliance work across teams rather than merely tracking tasks. In addition to pre-built sample workflows — such as automatically setting default freshness on a control or updating freshness upon proof upload — you can build custom, automated workflows tailored to your operation processes.

The Impact: Slash time spent on manual processes by 50% and save up to $150,000 annually on control orchestration.

Hierarchical Scopes to scale multi-entity compliance without duplication

As organizations grow, compliance programs expand across entities, business units, product lines, systems, and geographies. Hyperproof created Hierarchical Scopes to enable multi-level scope structures that reflect real enterprise architecture, giving you a clearer, more scalable way to manage programs across complexity.

With Hierarchical Scopes you can:

- Set control ownership at every level to give business units operational autonomy with centralized accountability.

- Roll up program health to give leadership real-time visibility across the entire enterprise.

- Configure granular permissions so team members see only the controls they own.

- Aggregate proof, evidence, and tasks upward through up to 10 levels of organizational hierarchy.

The Impact: Eliminate workarounds, scale seamlessly through M&A or expansion, and maintain a single source of truth.

Hyperproof is recognized as a category leader in the Enterprise GRC Chartis RiskTech Quadrant.

Third-party audit support that anticipates the auditor

Hyperproof’s third-party audit support streamlines audits and accelerates evidence collection, saving time and money.

Hyperproof eliminates traditional document requests over email or shared folders, resolving version-control issues and communication friction. By linking Hyperproof directly to ITSM systems (like Jira) and SIEM solutions (like Splunk), incident records, change logs, and security alerts are extracted automatically into audit-ready evidence.

The Impact: Shift from reactive audit cycles to proactive, ongoing compliance operations. Walk into every audit prepared, eliminate redundant evidence requests, and reuse work seamlessly for your next assessment cycle.

OutSystems uses Hyperproof to save 100+ hours on evidence collection and unify 12 audits into a single assessment experience. Read the case study.

The industry’s first GRC maturity model

The Hyperproof GRC Maturity Model was the first of its kind in the industry. Developed by our own experts and leading industry practitioners, the model is a practical, vendor-agnostic roadmap to help you improve your GRC processes, enter new markets, and navigate evolving regulatory demands.

The Impact: Evaluate your GRC maturity in under 15 minutes with our free assessment, and receive concrete, actionable steps to advance your operations.

Acuity International reduced manual processes by 60% and gained 90%+ visibility into their compliance posture with Hyperproof. Read the case study.

Modern enterprise GRC powered by responsible AI

Hyperproof delivers the core capabilities expected in a modern GRC platform — compliance, risk management, TPRM, and policy management — supported by Hyperproof AI. Embedded directly into every workflow, Hyperproof AI acts as an assurance engine to discover gaps, validate evidence, and automate repetitive tasks with transparent, human-in-the-loop oversight.

The Impact: Learn how many hours you’ll save, how much staff time you can redeploy to strategic work, and your estimated risk reduction. Calculate your ROI with Hyperproof.

See the proof for yourself

Hyperproof is the intelligent GRC platform that helps you streamline compliance operations, mitigate risks, and build trust with customers and stakeholders in one centralized platform.

See the proof for yourself. Request a personalized demo to see the Hyperproof platform in action.
Ingest Status
Rejected
Dedupe hash
9590d1a2afa31935893b2e460bd55e13
Press Eligible Reason
JSON nicht lesbar - manuelle Pruefung noetig: Inhalt konnte nicht als JSON geparst werden
Source Name
Hyperproof
Original Summary

<p>Most GRC platforms were built as trackers, not operational systems. They log that work happened without doing anything to reduce the manual burden. Teams re-map the same controls every time a new framework enters scope, coordinate audit prep by hand across siloed departments, and get stuck flat-structuring compliance for an enterprise that&#8217;s anything but flat.&#160;...</p>
<p>The post <a href="https://hyperproof.io/resource/the-proof-is-in-the-platform-why-modern-… Proof Is In the Platform: Why Modern GRC Teams Choose Hyperproof Over Trackers</a> appeared first on <a href="https://hyperproof.io">Hyperproof</a>.</p&gt;

Image URL
https://hyperproof.io/wp-content/uploads/2026/10/Hyperproof_Blog_The-Proof-Is-In-The-Platform__Thumbnail_622x350.png
Source Node
Content Hash (SHA-256, erste 32 hex)
1e771b976bec5021bb066f27192276b6
How Hyperproof Professional Services Accelerates Time-to-Value of Your GRC Program
Image File
Original HTML

How Hyperproof Professional Services Accelerates Time-to-Value of Your GRC Program

To build a resilient GRC program, you need clean data, tailored framework configurations, fully trained teams, and an execution strategy built around how your organization actually operates.

Hyperproof Professional Services helps you build this resilient GRC program by bridging the gap between software purchase and true platform adoption. We stand by your team throughout your entire GRC journey — delivering ongoing support, new hire training, integration expertise, and more.

How our team accelerates your GRC journey

Our Professional Services team helps you shorten time-to-value without exhausting your internal bandwidth. Here is how we support your organization at every stage:

- Initial implementation: We bring deep domain expertise to anticipate edge cases, design scalable integrations, leverage advanced platform capabilities, and ensure your team is prepared for full adoption. Choose between Hands-on Implementation (we build for you based on your inputs and approvals) or Guided Implementation (you build, we advise).

- Onboarding and ongoing training: Onboarding doesn’t end at launch. We deliver structured, expert-led training sessions — from foundational platform navigation to advanced risk management workflows — ensuring new hires get up to speed quickly.

- Technology and integration support: Your technology stack is dynamic. As you onboard new tools, our team builds custom Hypersyncs, adds proof types to existing ones, and consults on APIs to automate evidence collection at scale.

- Data migration and clean-up: We clean, transform, and load your existing frameworks, controls, risks, and vendor data into Hyperproof so you start with accurate data, not a blank platform.

- Custom reporting and insights: We turn compliance data into executive decision-making tools by building tailored dashboards and reports in Power BI, Tableau, or your preferred BI platform.

- Ecosystem and advisory access: Tap into our network of vetted IT auditors, managed service providers, and risk advisors to conduct readiness assessments and execute complex framework transformations.

Hyperproof”s implementation team was fantastic. They were very hands-on and regularly checked in to see how I was doing.

Modular services tailored to your GRC maturity

Every organization’s GRC maturity and team bandwidth are unique. Hyperproof offers flexible, à la carte solutions that combine into a custom package suited to your immediate goals and long-term vision.

Beyond software setup, we construct custom documentation guides, quick-reference sheets, and short video walkthroughs tailored to your company’s unique terminology and workflows.

Recognized on G2 for Fastest Implementation, Hyperproof turns platform capabilities into real-world results with expert guidance and hands-on execution that drives speed, satisfaction, and long-term retention.

Let’s design a professional services plan tailored to where your organization is today — and where it’s headed. Contact our team to get a tailored quote for your organization.

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
c0db61ab6f58ac4ed1527afa349dc0dd
Press Eligible
Yes
Press Eligible Reason
Manuelle Prüfung nötig. Risiko: LOW. Flags: ['none']. Stichprobe: True
Source Name
Hyperproof
Original Summary

<p>To build a resilient GRC program, you need clean data, tailored framework configurations, fully trained teams, and an execution strategy built around how your organization actually operates.&#160; Hyperproof Professional Services helps you build this resilient GRC program by bridging the gap between software purchase and true platform adoption. We stand by your team throughout your...</p>
<p>The post <a href="https://hyperproof.io/resource/how-hyperproof-professional-services-acc… Hyperproof Professional Services Accelerates Time-to-Value of Your GRC Program</a> appeared first on <a href="https://hyperproof.io">Hyperproof</a>.</p&gt;

Image URL
https://hyperproof.io/wp-content/uploads/2026/10/Hyperproof_Blog_HYP-Services__Thumbnail_622x350.png
Source Node
Content Hash (SHA-256, erste 32 hex)
5ce7f84fb7787d4f698f9030e5c129aa
Build or Buy Your GRC? Why “Building On Top” Is the Real Strategy
Image File
Original HTML

Build or Buy Your GRC? Why “Building On Top” Is the Real Strategy

The “build vs. buy” debate has existed for decades. With the rapid evolution of generative AI, building custom tools initially appears easier than ever.

The GRC space is no exception. Seeking quick wins, many risk and compliance teams are attempting to build internal utilities using Claude, ChatGPT, or custom LLMs. But in enterprise environments, the real choice isn’t binary. Instead of “build vs. buy,” the strategic question facing CISOs and compliance leaders today is “build from scratch vs. build on top.”

The hidden costs of building in-house GRC

Building a custom GRC tool in-house offers a few initial advantages:

- Tailored workflows: Processes are customized to your exact internal terminology from day one.

- Private cloud control: Sensitive audit evidence, source code, and security configurations remain strictly within your private cloud environment.

- No framework licensing fees: Building avoids per-seat or per-framework commercial software licensing.

However, wrapping generic LLMs creates massive engineering overhead, security risks, and audit exposure. Without a native system of record, generic models suffer from hallucinated outputs and lack verifiable data lineage.

As a result, in-house AI projects often remain limited to narrow productivity tasks — such as summarizing vendor PDFs or drafting routine policy updates. Organizations struggle to successfully operationalize home-built AI for external-facing assurance where accuracy, auditor defensibility, and proven evidence are mandatory. Bridging this confidence gap requires moving beyond generic AI wrappers toward grounded, agentic AI engines connected directly to live systems of record.

Why “building on top” delivers strategic advantage

Adopting a purpose-built, extensible GRC platform gives teams a production-ready baseline while preserving the freedom to customize and extend.

Key benefits of extending an AI-powered GRC platform:

- Immediate time-to-value: Achieve compliance readiness in weeks rather than spending 6 to 12 months engineering custom agent pipelines and maintaining integration code.

- Configurable autonomy: Purpose-built platforms meet your team where your AI appetite is — offering low floors and high ceilings. Choose your exact level of autonomy, starting with automated suggestions and escalating to agentic execution with full human-in-the-loop control.

- Auditor-grade defensibility: External auditors and regulators do not accept unverified AI outputs. Purpose-built platforms combine automated evidence collection via pre-built connectors (AWS, Azure, Okta, GitHub) with clear audit trails showing model context and data lineage.

- Zero technical debt from framework updates: Regulations and standards evolve constantly. Purpose-built vendors continuously update control mappings and prompt logic, freeing your engineering team from perpetual maintenance.

- Rigorous compliance standards: Established vendors maintain SOC 2 Type II, ISO 27001, and strict data isolation standards across their AI infrastructure out of the box.

- Combined GRC and site reliability domain expertise: Purpose-built systems combine deep risk and compliance expertise with scalable cloud architecture.

Building on top: what you inherit out of the box

When you build on top of an enterprise GRC platform, you inherit essential core capabilities out of the box so your team can focus on proprietary workflows:

- Continuous controls monitoring: Automatically pulls evidence across cloud infrastructure, identity, HR, and code repositories to continuously verify control pass/fail status in real time.

- Cross-framework control mapping: Automatically maps controls and evidence across standards (e.g., SOC 2, ISO 27001, NIST, HIPAA, GDPR), preventing duplicate testing effort.

- Agentic AI architecture: Specialized AI agents orchestrate complex multi-step workflows with human oversight built in.

- Model Context Protocol (MCP): Includes support for MCP for AI-to-system communication to query custom databases or execute automated remediation actions.

- Intelligent vendor assessments: Triggers vendor reassessments automatically based on thresholds or timeframes, prioritizing vendors by tier and routing tasks through pre-built workflows, to keep reviews consistent, efficient, and fully auditable.

- Automated questionnaire response: Uses machine learning to auto-fill customer security questionnaires with near-100% accuracy from a verified control library.

ROI of adopting an AI-powered GRC platform

The strategic advantage: scaling GRC on Hyperproof

Hyperproof goes beyond basic task automation and generic LLM wrappers. By embedding intelligence across the entire GRC lifecycle — discovering gaps, validating evidence, advising next steps, and automating remediation — Hyperproof transforms compliance from a reactive cost center into a strategic growth engine.

Building on Hyperproof gives you an extensible, enterprise-grade system of record. You get instant access to 200+ pre-built integrations, continuous assurance, and open APIs to extend workflows as your organization scales. The result isn’t just efficiency; it’s a strategic advantage that helps your organization scale faster and grow confidently.

Request a demo to talk to our experts and see Hyperproof’s purpose-built, extensible GRC platform in action.

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
5d1acdab08b360880b2dfec580e4aa20
Press Eligible
Yes
Press Eligible Reason
Manuelle Prüfung nötig. Risiko: MEDIUM. Flags: ['numbers']. Stichprobe: False
Source Name
Hyperproof
Original Summary

<p>The &#8220;build vs. buy&#8221; debate has existed for decades. With the rapid evolution of generative AI, building custom tools initially appears easier than ever. The GRC space is no exception. Seeking quick wins, many risk and compliance teams are attempting to build internal utilities using Claude, ChatGPT, or custom LLMs. But in enterprise environments, the...</p>
<p>The post <a href="https://hyperproof.io/resource/build-or-buy-your-grc-why-building-on-to… or Buy Your GRC? Why “Building On Top” Is the Real Strategy</a> appeared first on <a href="https://hyperproof.io">Hyperproof</a>.</p&gt;

Image URL
https://hyperproof.io/wp-content/uploads/2026/10/Hyperproof_Blog_Build-vs-Buy_Thumbnail_622x350.png
Source Node
Content Hash (SHA-256, erste 32 hex)
16144a65485ddcec0cdc6f45c13e0468
AI in GRC: Friend or Foe?
Image File
Original HTML

AI in GRC: Friend or Foe?

Originally published in Business Reporter

Every executive leadership team is asking themselves the same question about artificial intelligence right now: is this a tool that makes us better, or a risk we haven’t fully priced in? In governance, risk, and compliance (GRC), that question directly impacts commercial performance. Get the answer wrong and a company either falls behind competitors moving faster, or exposes itself to failures it never saw coming.

The honest answer is that AI is both a genuine asset and a genuine risk, depending entirely on how a business chooses to deploy it. The organizations pulling ahead have figured out where AI belongs in governance and where it doesn’t. The ones falling behind are making one of a few predictable mistakes.

Mistake 1: Assuming AI can replace GRC tooling altogether

There’s a growing belief in some boardrooms that AI can be leveraged to replace and rebuild their existing compliance tooling. But in fact, it’s not one or the other. AI and a dedicated GRC platform work best together. Intelligent automation from an AI tool eliminates manual toil, while a traditional GRC platform serves as a unified system of record, providing the structured governance architecture needed to protect the enterprise.

AI tools are well-suited to the repetitive, evidence-heavy parts of governance. It excels at high-throughput evidence orchestration and cross-framework mapping — eliminating the duplicative control drag that increases workloads and inflates operational costs.

Crucially, AI workflow acceleration should not be confused with an enterprise system of record that a GRC platform can provide. While AI tools can dynamically process data and produce answers, they do not inherently persist as a structured, version-controlled source of truth. Long-term governance requires a permanent system of record to maintain policy versioning, centralize framework mappings, and retain the defensible audit trails that regulators and external auditors demand over time.

Mistake 2: Using AI as an alternative to human expertise

The next misconception about AI in GRC is that humans in the loop slow the process down. Some leaders assume the fastest path is to remove human review entirely and let the system run on its own. Defining what tasks are best performed by AI tools and what is best performed by human experts is crucial and urgent work.

Leaders must consider that AI cannot decide how much risk a business is willing to accept. It cannot weigh a new market opportunity against a partner’s security posture, or judge whether a control gap is a rounding error or a genuine threat to the business. Those decisions require context about strategy, appetite, and consequences that only an expert can bring. The businesses treating AI as a wholesale replacement for judgment are the ones most likely to get burned by it.

Deals close faster and markets open more easily when a business can show customers and partners a governance model that pairs AI speed with human accountability. Buyers, particularly at the enterprise level, are increasingly asking vendors to prove that AI-assisted decisions carry a real person’s name behind them. Oversight done well is not a brake on the business, but what earns the trust that closes the deal.

Mistake 3: Isolating AI governance into a standalone silo

A third mistake to avoid is treating AI governance as a specialized silo, owned by a separate team with its own tools and its own reporting line, disconnected from the rest of the business’s risk and compliance operations. This creates architectural friction and fragmented risk registers, leaving leadership without continuous, real-time risk visibility.

This feels tidy on an org chart, but in practice can create blind spots. When AI risk lives apart from the rest of the business’s control environment, leadership ends up with two incomplete pictures instead of one complete operating view. A company embedding AI oversight directly into its existing governance operations can scale AI adoption with confidence, because the same standards, reporting, and accountability already in place for every other business risk simply extend to cover it.

Mistake 4: Believing fully AI-generated work will pass an audit

The belief that AI-generated compliance work, on its own, is sufficient to pass regulatory scrutiny is unrealistic. Auditors and regulators consistently ask not just what a system concluded, but how it got there, and who signed off on it. Crucially, an audit exists to affirm the specific policies and controls that business leaders choose to operate under. Executive leadership remains fundamentally responsible for enterprise risk and performance, and that accountability cannot be outsourced to an algorithm.

A black box that spits out risk scores without a traceable explanation fails under real scrutiny. True defensibility comes from leveraging AI for evidence testing and pattern detection, paired with documented human review that actively challenges, validates, and approves the results.

AI makes a great co-pilot, not a CISO

With all that being said, none of this makes AI a threat to governance professionals. The technology itself is neither friend nor foe. What determines the outcome is the operating model a business builds around it: a thoughtful design for how AI, humans, and systems of record will work together.

The companies getting this right prove to their customers and partners that they can move at the speed AI enables without losing the accountability that earns trust. That combination — speed paired with defensibility — is quickly becoming a real differentiator in how enterprises win business from one another.

Curious how the best GRC and security leaders are actually thinking about risk? Step into their shoes by playing CISO for a Day, Hyperproof’s interactive challenge that puts you in the decision seat, at hyperproof.io/ciso-for-a-day-game/.

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
778a8f485b2bd0b232364f5ce90b101d
Press Eligible
Yes
Press Eligible Reason
Discusses enterprise AI governance, risk, and compliance practices.
Source Name
Hyperproof
Original Summary

<p>Originally published in Business Reporter Every executive leadership team is asking themselves the same question about artificial intelligence right now: is this a tool that makes us better, or a risk we haven&#8217;t fully priced in? In governance, risk, and compliance (GRC), that question directly impacts commercial performance. Get the answer wrong and a company...</p>
<p>The post <a href="https://hyperproof.io/resource/ai-in-grc-friend-or-foe/">AI in GRC: Friend or Foe?</a> appeared first on <a href="https://hyperproof.io">Hyperproof</a>.</p&gt;

Image URL
https://hyperproof.io/wp-content/uploads/2026/10/Hyperproof_Blog_AI-in-GRC_Thumbnail_622x350.png
Source Node
Content Hash (SHA-256, erste 32 hex)
22ff6acb7de1d574b735df1adb03eaab
Hyperproof and Carahsoft Partner to Introduce Modern GRC Solutions Across the Federal and Public Sector
Image File
Original HTML

Hyperproof and Carahsoft Partner to Introduce Modern GRC Solutions Across the Federal and Public Sector

Hyperproof, a leading modern enterprise GRC platform, and Carahsoft Technology Corp., The Trusted Government IT Solutions Provider®, today announced a partnership. Under the agreement, Carahsoft will serve as Hyperproof’s Master Government Aggregator®, making Hyperproof’s GRC automation, continuous compliance and risk management solutions available to Public Sector organizations, defense industrial base (DIB) suppliers and Government contractors through Carahsoft’s reseller partners and NASA Solutions for Enterprise-Wide Procurement (SEWP) V, National Association of State Procurement Officials (NASPO) ValuePoint, The Interlocal Purchasing System (TIPS), OMNIA Partners, E&I Cooperative Services Contract and The Quilt contracts.

“Public Sector organizations and contractors face immense pressure to keep pace with rigorous frameworks like CMMC,” said Craig Unger, CEO and Founder of Hyperproof. “Partnering with Carahsoft allows us to extend our reach into the Government sector with a trusted partner who understands the unique procurement and compliance needs of public institutions. Together, we are helping organizations replace spreadsheet-driven workflows with continuous, defensible assurance.”

As Federal agencies and Government suppliers navigate evolving security standards — such as the changing timeline for the Cybersecurity Maturity Model Certification (CMMC) program — the administrative burden of manual evidence collection and control tracking often bogs down operations. Importantly, Hyperproof is the only GRC platform that is both Federal Risk and Authorization Management Program (FedRAMP®) Class C Certified (rev5) and purpose-built for the operational complexity of enterprise-grade CMMC programs.

The partnership unites Hyperproof’s scalable control operations and integrated risk management with Carahsoft’s reach and Federal market expertise, giving Public Sector organizations a streamlined path to achieving and maintaining continuous audit readiness. Hyperproof and Carahsoft deliver a complete end-to-end strategy for CMMC and FedRAMP compliance, combining domain expertise with automated workflows that turn static assessments into dynamic, real-time risk oversight.

“Government agencies are increasingly looking for ways to simplify and automate the complex processes required to maintain CMMC, FedRAMP and other evolving compliance requirements,” said Brian O’Donnell, Vice President of Cybersecurity Solutions at Carahsoft. “Hyperproof’s modern approach to GRC automation and continuous compliance strengthens our portfolio with a solution designed to help organizations streamline evidence collection, manage controls and maintain ongoing audit readiness. We are pleased to partner with Hyperproof to bring these capabilities to our reseller partners and the Government market, helping Public Sector organizations and contractors more efficiently manage risk and meet their compliance obligations.”

Through this partnership, Public Sector teams can scale a common control set across complex operating divisions, automate evidence collection and map controls across CMMC, FedRAMP, NIST SP 800-53, NIST SP 800-171 and custom Government frameworks.

Hyperproof’s offerings are available through Carahsoft’s SEWP V contracts NNG15SC03B and NNG15SC27B, NASPO ValuePoint Master Agreement #AR2472, TIPS Contract #220105, OMNIA Partners Contract #R240303, E&I Contract #EI00063~2021MA and The Quilt Master Service Agreement Number MSA05012019-F. For more information contact the Carahsoft Team at (844) 445-5688 or [email protected]; or learn more about Hyperproof’s solutions here.

About Hyperproof

Hyperproof is a modern, AI-powered GRC platform that helps IT, security, and compliance teams manage risk, streamline compliance operations, and build trust with customers and partners. The Hyperproof platform enables organizations to manage controls at scale, automate evidence collection, orchestrate risk workflows, and centralize third-party risk management in one unified system. With Hyperproof, teams can scale compliance across the business, connect controls to risks, automate security questionnaires, and maintain continuous visibility across their security and vendor ecosystems. Leading organizations such as Reddit, Fortinet, Appian, Outreach, and Thales trust Hyperproof to modernize governance and compliance operations. To learn more about Hyperproof, visit hyperproof.io.

Contact

Craig Unger

CEO and Founder, Hyperproof

[email protected] 

About Carahsoft’s Cybersecurity Solutions Portfolio

Carahsoft’s Cybersecurity solutions portfolio includes leading and emerging technology vendors who enable organizations to defend against cyber threats, manage risk and achieve compliance. Supported by dedicated cybersecurity product specialists and an extensive ecosystem of resellers, integrators and service providers, we help organizations identify the right technology for unique environments and provide access to technology solutions through our broad portfolio of contract vehicles. The cybersecurity portfolio spans solutions for Supply Chain Risk Management, Cloud Security, Zero Trust, Network & Infrastructure, Identity & Access Management, Risk & Compliance and more, ensuring comprehensive protection for organizations’ cyber ecosystems. Explore Carahsoft’s Cybersecurity Solutions for Government here.

About Carahsoft

Carahsoft Technology Corp. is The Trusted Government IT Solutions Provider, supporting Public Sector organizations across Federal, State and Local Government agencies and Education and Healthcare markets. As the Master Government Aggregator for our vendor partners, we deliver solutions for Cybersecurity, MultiCloud, DevSecOps, Artificial Intelligence, Customer Experience and Engagement, Open Source and more. Working with resellers, systems integrators and consultants, our sales and marketing teams provide industry leading IT products, services and training through hundreds of contract vehicles. Visit us at www.carahsoft.com.

Contact

Mary Lange

(703) 230-7434

[email protected]

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
79ca31d49296d77ac9d259485062591f
Press Eligible
Yes
Press Eligible Reason
Business partnership expanding enterprise GRC and compliance solutions to government and public-sector organizations.
Source Name
Hyperproof
Original Summary

<p>Hyperproof, a leading modern enterprise GRC platform, and Carahsoft Technology Corp., The Trusted Government IT Solutions Provider®, today announced a partnership. Under the agreement, Carahsoft will serve as Hyperproof&#8217;s Master Government Aggregator®, making Hyperproof’s GRC automation, continuous compliance and risk management solutions available to Public Sector organizations, defense industrial base (DIB) suppliers and Government contractors...</p>
<p>The post <a href="https://hyperproof.io/resource/hyperproof-and-carahsoft-partner-to-intr… and Carahsoft Partner to Introduce Modern GRC Solutions Across the Federal and Public Sector</a> appeared first on <a href="https://hyperproof.io">Hyperproof</a>.</p&gt;

Image URL
https://hyperproof.io/wp-content/uploads/2026/10/Hyperproof_Blog_Carahsoft-press-release_Thumbnail_622x350.png
Source Node
Content Hash (SHA-256, erste 32 hex)
604333ad8bb4c3fa5e6cc154ce8b0c00
Measuring What Matters in Third-Party Risk: From Assessment Volume to Business Exposure
Image File
Original HTML

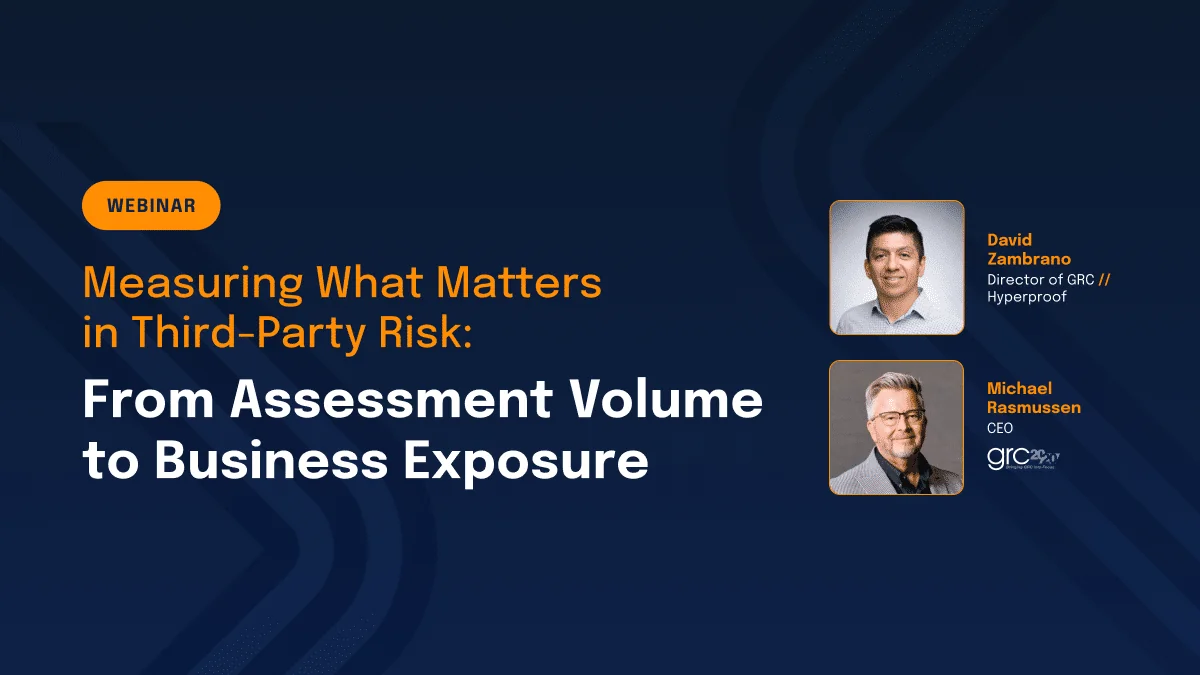
Measuring What Matters in Third-Party Risk: From Assessment Volume to Business Exposure

November 17th at 12 PM ET / 9 AM PT

Most TPRM programs can report how many vendor assessments they completed last quarter. Fewer can show whether those assessments actually reduced risk. When scoring varies by reviewer, evidence goes stale between review cycles, and remediation isn’t tracked to completion, completion counts reveal very little about an organization’s vendor risk posture.

Join Michael Rasmussen of GRC 20/20 Research and David Zambrano, Director of GRC at Hyperproof, to learn how to align TPRM metrics with business impact. Michael will share his research on why vendor criticality and exposure matter more than assessment volume. David will explain how GRC teams use AI-powered assessments and a centralized system of record to measure and report vendor risk with confidence.

What we cover:

Activity vs. outcomes: Why completion counts fall short, and how to track the shift from inherent to residual risk

Criticality beyond spend: Why contract value is a weak proxy for vendor risk, and how to prioritize based on data access and the services a vendor supports

Consistency as a prerequisite: How standardized, AI-assisted assessments make vendor risk comparable across teams and business units

Closing the gap between reviews: How continuous monitoring and remediation tracking keep vendor risk data current between assessment cycles

Board-ready reporting: How to present TPRM as a strategic capability backed by defensible, auditable risk data

Learn how to measure your third-party risk program by the risk it reduces, and give leadership the confidence to act.

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
c615f5bfa801c76af2dabf4264c7a361
Press Eligible
Yes
Press Eligible Reason
Promotional webinar with substantive content on enterprise third-party risk management and GRC metrics.
Source Name
Hyperproof
Original Summary

<p>November 17th at 12 PM ET / 9 AM PT Most TPRM programs can report how many vendor assessments they completed last quarter. Fewer can show whether those assessments actually reduced risk. When scoring varies by reviewer, evidence goes stale between review cycles, and remediation isn&#8217;t tracked to completion, completion counts reveal very little about...</p>
<p>The post <a href="https://hyperproof.io/resource/measuring-what-matters-in-third-party-ri… What Matters in Third-Party Risk: From Assessment Volume to Business Exposure</a> appeared first on <a href="https://hyperproof.io">Hyperproof</a>.</p&gt;

Image URL
https://hyperproof.io/wp-content/uploads/2026/10/Hyperproof_WEB_Thumbnail_Webinar_1200x675_November-TPRM_PRE-101226.png
Source Node
Content Hash (SHA-256, erste 32 hex)
b9c90a6b2fc4db77fdb5621480aaa887
The Future of Compliance in Africa: The Role of Technology, AI and Regulatory Change
Image File
Original HTML

On-Demand

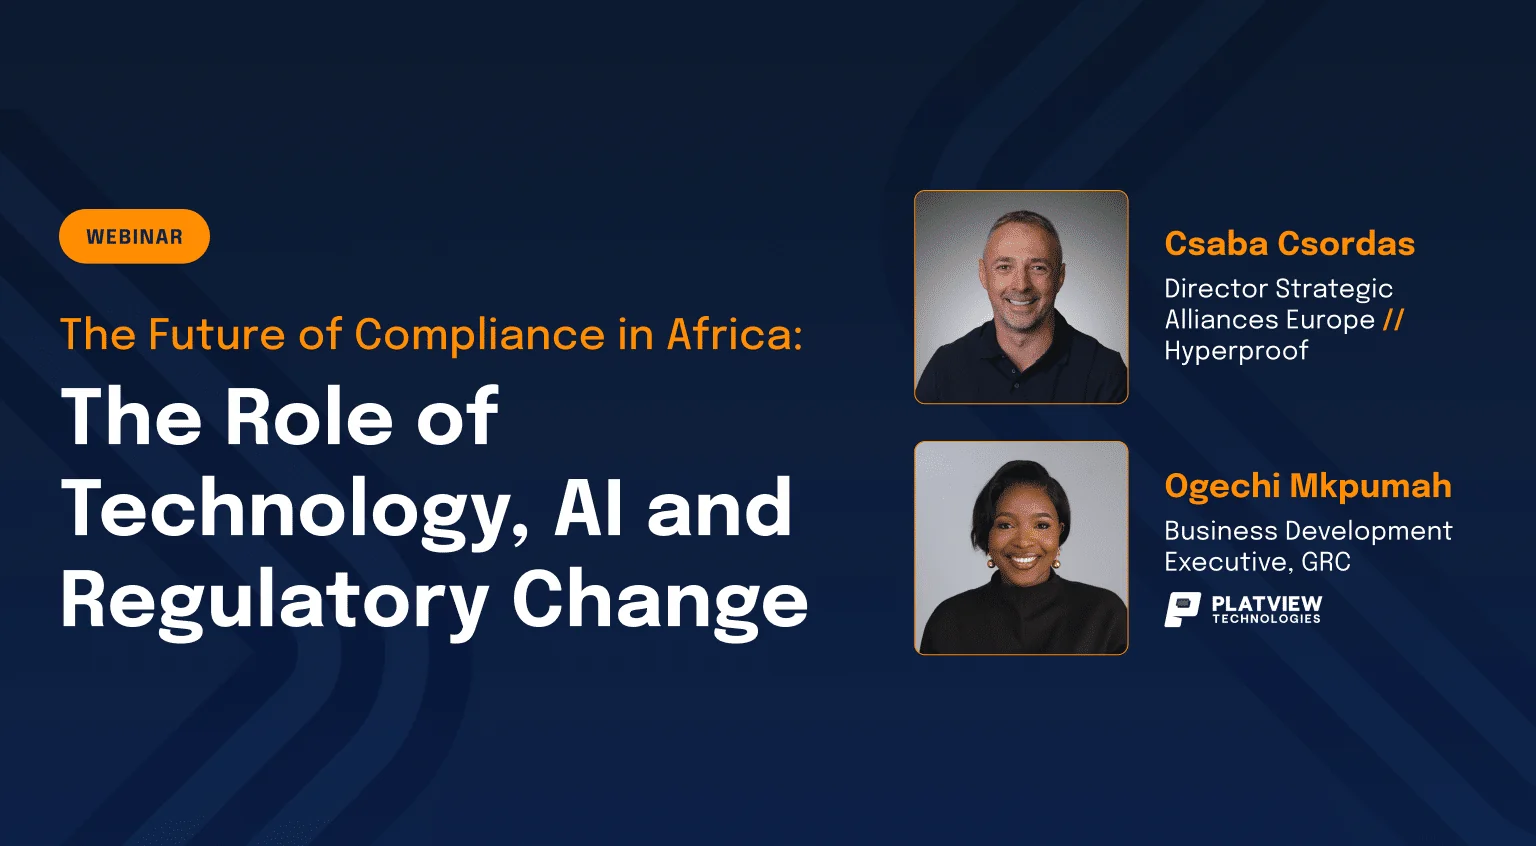
The Future of Compliance in Africa: The Role of Technology, AI and Regulatory Change

Regulation around data security and AI is tightening worldwide, and organisations operating in and with Africa are feeling the effects. New EU rules reach well beyond Europe’s borders. Meanwhile, African regulators are building their own frameworks at pace. Financial services firms, national service providers, and businesses of every kind now face growing pressure to show they are compliant, secure, and ready for AI.

Join Hyperproof and Platview for a practical session on what this changing landscape means for your organisation. We’ll look at the global regulatory picture and the specific challenges facing African businesses. We’ll also show how the right combination of expertise and technology can turn compliance from a burden into a strength.

What we cover:

Ogechi Mkpumah, Business Development Executive, GRC

Platview

Csaba Csordas, Director Strategic Alliances Europe

Hyperproof

Class (B2B/B2C)
B2B
Ingest Status
Rewritten
Dedupe hash
e17e22caf0ece96210f8a3caf71f94de
Press Eligible
Yes
Press Eligible Reason
Business-focused session on compliance technology, AI, and regulatory changes affecting African organizations.
Source Name
Hyperproof
Original Summary

<p>Regulation around data security and AI is tightening worldwide, and organisations operating in and with Africa are feeling the effects. New EU rules reach well beyond Europe&#8217;s borders. Meanwhile, African regulators are building their own frameworks at pace. Financial services firms, national service providers, and businesses of every kind now face growing pressure to show...</p>
<p>The post <a href="https://hyperproof.io/resource/the-future-of-compliance-in-africa/">The Future of Compliance in Africa: The Role of Technology, AI and Regulatory Change</a> appeared first on <a href="https://hyperproof.io">Hyperproof</a>.</p&gt;

Image URL
https://hyperproof.io/wp-content/uploads/2026/10/Hyperproof_WEB_Thumbnail_Webinar_1536x846_Compliance-In-Africa-100626.png
Source Node
Content Hash (SHA-256, erste 32 hex)
daed98b1cc3658a6522834d8d07ce42f
Capitol Hill Meetings on Your Own
Original HTML

Skip to main content

User account menu

Log In

Engage

Join

Shop

Subscribe

Suppliers

Jobs

Contact

My Account

Powering Strong Communities

Main navigation

About

About

The Association

Value of APPA

Members

Member Directory

JAAs & State Associations

Corporate Associate Members

Join

Leadership & Board

Careers with APPA

Newsroom

Public Power

What Is Public Power?

Where Is Public Power?

Stats and Facts

Electricity Basics

Forming a Public Power Utility

Promoting Public Power

Protecting Public Power

Utility Jobs

Issues & Policy

Issues & Policy

Key Issues

Maintain Affordability

Electric Reliability

Permitting Reform

Mitigate Wildfires

Supporting FEMA

Regulatory

Energy Regulation Filings

Environment Filings

Take Action

Resolutions

PowerPAC

Legislative Rally

Policy Makers Council

Programs & Services

Programs & Services

Energy Innovation

Grants and Scholarships

Research and Development

Grid Security

Cyber and Physical Security

Cybersecurity Accelerator Program

Mutual Aid and Emergency Response

Wildfire Mitigation Planning

Risk Management

Benchmarking & Operations

Reliable Public Power Provider

Smart Energy Provider

PowerTRX Reliability

Safety

PowerTRX Safety

Surveys and Survey Reports

Utility Operational Excellence Guide

Awards

APPA Academy

APPA Academy

In-Person Events

Customer Connections Conference

Joint Action Conference

Online Events

Courses & Webinars

On-Demand Library

Events Calendar

Coaching & Advisory Services

Sponsor & Exhibit

In-House Training

News

News

Public Power Current newsletter

Public Power Magazine

Podcasts

Advertising

Newsroom

For Members

For Members

Member Welcome Center

Utility Member Benefits Quick Reference

Utility Member Handbook

Featured Products

CEERUM Energy Planning Tool

Monster Detective Collective

PowerTRX Pro

Public Power Data Source

Resources

Artificial Intelligence

Awards

Data Centers

DEED R&D

Energy Tax Credits for Utilities

Governance

Member Directory

Mutual Aid/Emergency Response

Promoting Public Power

Utility Operational Excellence Guide

Surveys & Survey Reports

APPA Engage

Vendor Opportunities: RFP Portal

User account menu

Log In

Engage

Join

Shop

Subscribe

Suppliers

Jobs

Contact

My Account

Search

You are here

Home

Capitol Hill Meetings on Your Own

Wed, 03/03/2027 - 21:00

Wed, 03/03/2027 - 17:00

Ingest Status
Rejected
Dedupe hash
17d95fec03625385fbfd877b277e91a7
Source Name
APPA Newsroom
Original Summary

<span>Capitol Hill Meetings on Your Own</span>
<span><span lang="lang">jbedbury</span></span>
<span><time datetime="2026-10-19T14:18:00-04:00" title="October 19, 2026, 02:18 PM">Mon, 10/19/2026 - 14:18</time>
</span>
<div class="field field-node--field-event-start-date field-name-field-event-start-date field-type-datetime field-label-hidden">
<div class="field-items">
<div class="field-item"><time datetime="2027-03-04T02:00:00Z">Wed, 03/03/2027 - 21:00</time>
</div>
</div>
</div>
<div class="field field-node--field-event-end-date field-name-field-event-end-date field-type-datetime field-label-hidden">
<div class="field-items">
<div class="field-item"><time datetime="2027-03-03T22:00:00Z">Wed, 03/03/2027 - 17:00</time>
</div>
</div>
</div>
<div class="field field-node--field-featured field-name-field-featured field-type-boolean field-label-above">
<div class="field-label">Featured</div>
<div class="field-items">
<div class="fi

Source Node
Content Hash (SHA-256, erste 32 hex)
314d68a62742ff5d1e13b51559ca52d7
Break
Original HTML

Skip to main content

User account menu

Log In

Engage

Join

Shop

Subscribe

Suppliers

Jobs

Contact

My Account

Powering Strong Communities

Main navigation

About

About

The Association

Value of APPA

Members

Member Directory

JAAs & State Associations

Corporate Associate Members

Join

Leadership & Board

Careers with APPA

Newsroom

Public Power

What Is Public Power?

Where Is Public Power?

Stats and Facts

Electricity Basics

Forming a Public Power Utility

Promoting Public Power

Protecting Public Power

Utility Jobs

Issues & Policy

Issues & Policy

Key Issues

Maintain Affordability

Electric Reliability

Permitting Reform

Mitigate Wildfires

Supporting FEMA

Regulatory

Energy Regulation Filings

Environment Filings

Take Action

Resolutions

PowerPAC

Legislative Rally

Policy Makers Council

Programs & Services

Programs & Services

Energy Innovation

Grants and Scholarships

Research and Development

Grid Security

Cyber and Physical Security

Cybersecurity Accelerator Program

Mutual Aid and Emergency Response

Wildfire Mitigation Planning

Risk Management

Benchmarking & Operations

Reliable Public Power Provider

Smart Energy Provider

PowerTRX Reliability

Safety

PowerTRX Safety

Surveys and Survey Reports

Utility Operational Excellence Guide

Awards

APPA Academy

APPA Academy

In-Person Events

Customer Connections Conference

Joint Action Conference

Online Events

Courses & Webinars

On-Demand Library

Events Calendar

Coaching & Advisory Services

Sponsor & Exhibit

In-House Training

News

News

Public Power Current newsletter

Public Power Magazine

Podcasts

Advertising

Newsroom

For Members

For Members

Member Welcome Center

Utility Member Benefits Quick Reference

Utility Member Handbook

Featured Products

CEERUM Energy Planning Tool

Monster Detective Collective

PowerTRX Pro

Public Power Data Source

Resources

Artificial Intelligence

Awards

Data Centers

DEED R&D

Energy Tax Credits for Utilities

Governance

Member Directory

Mutual Aid/Emergency Response

Promoting Public Power

Utility Operational Excellence Guide

Surveys & Survey Reports

APPA Engage

Vendor Opportunities: RFP Portal

User account menu

Log In

Engage

Join

Shop

Subscribe

Suppliers

Jobs

Contact

My Account

Search

You are here

Home

Break

Tue, 02/09/2027 - 10:00

Tue, 02/09/2027 - 10:15

Class (B2B/B2C)
Ignore
Ingest Status
Need Review
Dedupe hash
ac3847d40edc8ccd107d0e58e880dd1a
Press Eligible
No
Press Eligible Reason
Irrelevant (need review): The page contains navigation text and no substantive article content.
Source Name
APPA Newsroom
Original Summary

<span>Break</span>
<span><span lang="lang">jbedbury</span></span>
<span><time datetime="2026-10-22T10:34:39-04:00" title="October 22, 2026, 10:34 AM">Thu, 10/22/2026 - 10:34</time>
</span>
<div class="field field-node--field-event-start-date field-name-field-event-start-date field-type-datetime field-label-hidden">
<div class="field-items">
<div class="field-item"><time datetime="2027-02-09T15:00:00Z">Tue, 02/09/2027 - 10:00</time>
</div>
</div>
</div>
<div class="field field-node--field-event-end-date field-name-field-event-end-date field-type-datetime field-label-hidden">
<div class="field-items">
<div class="field-item"><time datetime="2027-02-09T15:15:00Z">Tue, 02/09/2027 - 10:15</time>
</div>
</div>
</div>
<div class="field field-node--field-featured field-name-field-featured field-type-boolean field-label-above">
<div class="field-label">Featured</div>
<div class="field-items">
<div class="field-item">Off</div>
</

Source Node
Content Hash (SHA-256, erste 32 hex)
314d68a62742ff5d1e13b51559ca52d7
Building the Workforce and Leadership Bench Public Power Needs
Original HTML

Attracting, developing, and retaining talent remains one of the most significant challenges facing public power utilities. This session will explore strategies for succession planning, workforce development, leadership training, and knowledge transfer. Panelists will discuss how they are building strong organizational cultures, preparing future leaders, and ensuring their utilities have the skills and expertise needed to meet future demands.

Carrie Meek Gallagher, CEO, Long Island Power Authority, New York

Class (B2B/B2C)
Ignore
Ingest Status
Rejected
Dedupe hash
5f08aabc08ef47dc488824aa3c7d13fc
Press Eligible
No
Press Eligible Reason
Text too short (68 words. Min: 150)
Source Name
APPA Newsroom
Original Summary

<span>Building the Workforce and Leadership Bench Public Power Needs</span>
<span><span lang="lang">jbedbury</span></span>
<span><time datetime="2026-10-22T10:34:43-04:00" title="October 22, 2026, 10:34 AM">Thu, 10/22/2026 - 10:34</time>
</span>
<div class="body field field-node--body field-name-body field-type-text-with-summary field-label-hidden">
<div class="field-items">
<div class="field-item"><p>Attracting, developing, and retaining talent remains one of the most significant challenges facing public power utilities. This session will explore strategies for succession planning, workforce development, leadership training, and knowledge transfer. Panelists will discuss how they are building strong organizational cultures, preparing future leaders, and ensuring their utilities have the skills and expertise needed to meet future demands.</p><p><em><strong>Carrie Meek Gallagher</strong>, CEO, Long Island Power Authority, New York</em></p></div>
</div>
</div>
<div c

Source Node
Content Hash (SHA-256, erste 32 hex)
101fcb848987aa71ba02fe1887e235e0