By Editor , 27 October 2026
Two PHP RCE Flaws Expose ~2 Million Servers; 99.99% Unpatched

Global – October 27, 2026 -- Roughly 2,000,000 internet-facing PHP servers run versions affected by two critical remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, and 99.99% of identifiable servers remain unpatched, according to Shodan data cited by OX Security.

The PHP core team issued an out-of-band security release fixing both flaws in versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Shodan counts only servers that expose their PHP version, so the real total is likely higher.
By Editor , 27 October 2026
Malicious LiteLLM 1.107.0 on PyPI Steals AI Keys, Installs RAT

Global -- A malicious version of LiteLLM, version 1.107.0, was published to PyPI on October 21, 2026. It bundles a credential-stealing infostealer with a remote access trojan (RAT), according to OX Security. It is the second hijacking of the AI gateway this year, and PyPI has since quarantined the release.

By Editor , 27 October 2026
Three CVSS 9.2 Pillow Flaws Enable Code Execution via Image Upload

Global – October 27, 2026 -- Three critical vulnerabilities rated CVSS 9.2 in Pillow, the Python imaging library with an estimated 436 million monthly downloads, let a single crafted EPS, TIFF or JPEG file trigger command execution or heap corruption in any Python service that processes user-supplied images. Disclosed on 2026-10-19, all three flaws are fixed in Pillow 13.0.0.

By Editor , 27 October 2026
Node.js Patches Brotli Flaw Enabling Remote Code Execution

Global -- Node.js issued security releases across all supported lines on October 21, 2026, to fix CVE-2026-111497, a high-severity out-of-bounds write in its bundled Brotli decoder that can lead to remote code execution. A Node.js process that decompresses attacker-controlled Brotli data, including Brotli-encoded HTTP responses it fetches, can be driven to write past the end of its buffer. The result is leaked memory or code execution with the process's privileges.

By Editor , 27 October 2026
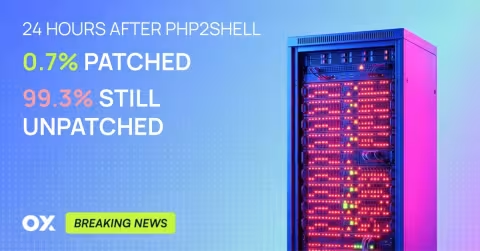
99.3% of Exposed PHP Hosts Unpatched 24 Hours After PHP2Shell Fix

GLOBAL – October 27, 2026 -- Only 14,151 of 1,974,890 measurable PHP instances in the affected version range showed a patched release 24 hours after PHP shipped emergency fixes for the PHP2Shell flaws, leaving 99.3% exposed, according to OX Security.

PHP released the fixes on October 21 for CVE-2026-109618 and CVE-2026-109619. Both are critical vulnerabilities that allow unauthenticated remote code execution in the PHP engine itself. Governments and security agencies urged organizations to patch immediately, and some organizations took systems offline.

By Editor , 27 October 2026
93.6% of PHP Hosts Still Exposed to PHP2Shell Five Days After Fix

Global – October 27, 2026 -- Five days after the PHP project shipped emergency fixes for the PHP2Shell flaws, 93.6% of measurable PHP instances remain exposed, according to OX Security scans run through October 26, 2026. That is roughly 15 of every 16 hosts the firm can measure.

By Editor , 27 October 2026
Security Tool Sprawl: 65% of Leaders Report Too Many Tools

Global – October 27, 2026 -- Sixty-five percent of 2,000 senior security decision-makers say they have too many security tools or vendors, and 53% say their tools can't be integrated, according to 2025 research by Barracuda and Vanson Bourne. For application security (AppSec) teams, the sprawl shows up as overlapping findings from static application security testing (SAST), software composition analysis (SCA), and cloud-native application protection platforms (CNAPPs).

By Editor , 27 October 2026
Xerox Named Leader in IDC MarketScape for Mailroom Solutions 2026

Norwalk – October 27, 2026 -- Xerox Holdings Corporation (NASDAQ: XRX) has been named a Leader in the IDC MarketScape: Worldwide Mailroom Solutions and Services 2026 Vendor Assessment. The report evaluates how well vendors help organizations modernize mailroom operations through intelligent automation, information governance, workflow integration and digital transformation.

By Editor , 27 October 2026
Xerox Named Leader in Quocirca Print Security Landscape 2026

Norwalk, Conn. – October 27, 2026 -- Xerox has been named a Leader in Quocirca's Print Security Landscape 2026, an independent assessment of how leading print manufacturers help organizations counter cybersecurity risks across print and document environments.